Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
ConnectWise Warns ScreenConnect Attacks Continue as SCKit Targets Unpatched Systems
ConnectWise on Monday said it completed its investigation into unauthorized access targeting partner ScreenConnect environments, and recommended customers to ensure...
 ANWENDUNGSSICHERHEIT
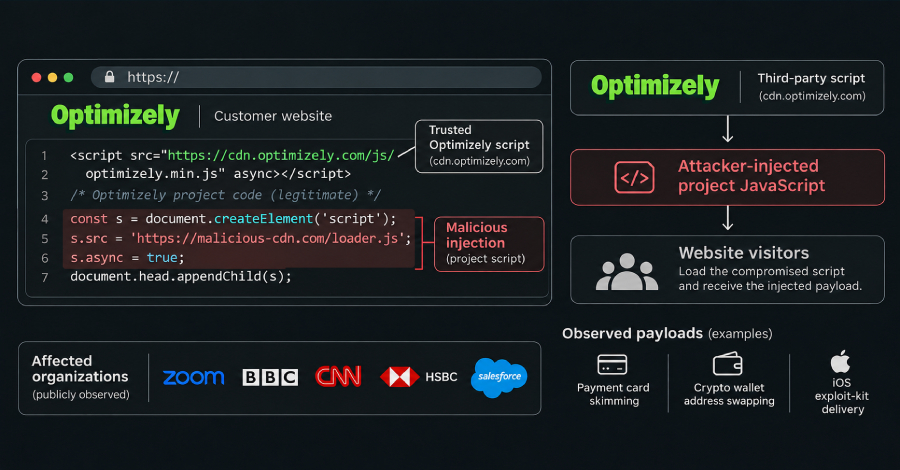
Hijacked Optimizely Scripts Served Card Skimmer and iOS Exploit Kits to CNN, BBC and Zoom Visitors
An attacker exploited a flaw in Optimizely Web Experimentation to plant malicious code in some of the scripts that customers'...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-125447: High Schwachstelle
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Kaliforms Kali Forms kali-forms allows Reflected XSS.This issue...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-125828: High Schwachstelle
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Liquid Web / StellarWP BookIt bookit allows Stored...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-125813: High Schwachstelle
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Ays Pro Survey Maker survey-maker allows Reflected XSS.This...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-125791: High Schwachstelle
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in iWorks Orphans sierotki allows Stored XSS.This issue affects...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-125790: High Schwachstelle
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in e4jvikwp VikBooking Hotel Booking Engine & PMS vikbooking...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-125789: High Schwachstelle
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in e4jvikwp VikBooking Hotel Booking Engine & PMS vikbooking...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-125775: High Schwachstelle
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in CRM Perks CRM Perks Forms crm-perks-forms allows Reflected...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-125764: High Schwachstelle
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in E2Pdf.com e2pdf e2pdf allows Stored XSS.This issue affects...