Cloud-Sicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-55723: High Luecke in F5 Nginx_Ingress_Controller
When NGINX Ingress Controller is configured with Custom Resource Definitions (CRDs) or Ingress annotations, an injection vulnerability exists in the...
 CLOUD-SICHERHEIT
🟠 CVE-2026-15583: High Schwachstelle
A confused-deputy flaw in Grafana MCP Server allows an unauthenticated remote attacker to exfiltrate the server's environment-configured Grafana service-account token...
 CLOUD-SICHERHEIT
SASE Has An AI Blind Spot. Inspecting Packets Is No Longer Enough.
For years, routing traffic through cloud proxies was good enough. Then work moved to the browser, AI entered the workflow,...
 CLOUD-SICHERHEIT
Firefox, Chrome, Adobe, and VMware Updates Fix Multiple Critical Security Flaws
Mozilla has released updates to address two critical flaws in Firefox for which it warned that exploit code has been...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-12707: High Schwachstelle
Summary Cloudflare quiche was discovered to be vulnerable to memory resource exhaustion due to unbounded queuing of post-handshake client migration...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-12523: High Schwachstelle
Summary Cloudflare quiche's HTTP/3 layer was discovered to be vulnerable to resource exhaustion (i.e., memory) by means of specially crafted...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-15416: High Schwachstelle
A flaw was identified in Argo CD, the GitOps engine used by Red Hat OpenShift GitOps, that could allow an...
 CLOUD-SICHERHEIT
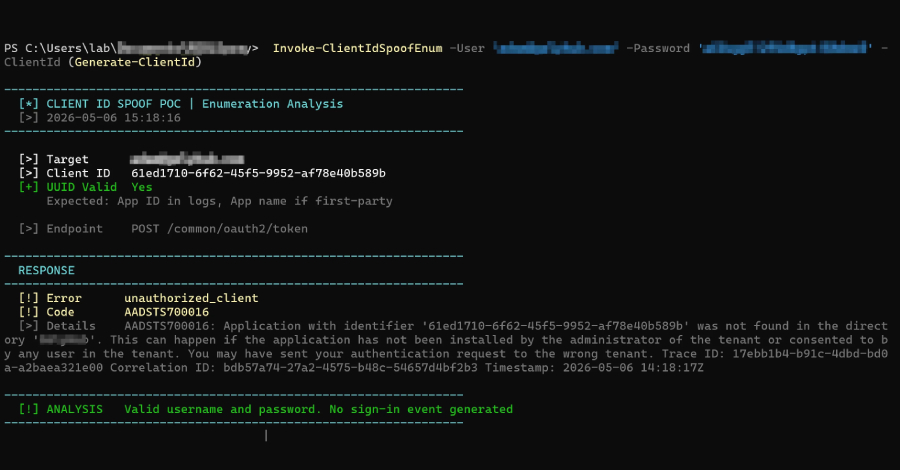
OAuth Client ID Spoofing Lets Attackers Validate Stolen Microsoft Entra Credentials
At least two distinct threat actors are weaponizing a novel evasion technique called OAuth client ID spoofing in cloud campaigns,...
 CLOUD-SICHERHEIT
RabbitMQ Flaws Could Leak OAuth Secrets and Expose Cross-Tenant Queue Metadata
Cybersecurity researchers have disclosed details of two access control-related flaws impacting the RabbitMQ message broker service that could allow attackers...
CLOUD-SICHERHEIT
🟡 CVE-2026-49876: Medium Luecke in Apache Gravitino
Authenticated SSRF in Gravitino JobManager allows server-side HTTP requests to internal network and cloud metadata endpoints via unvalidated job template...