Endpunktsicherheit
 ENDPUNKTSICHERHEIT
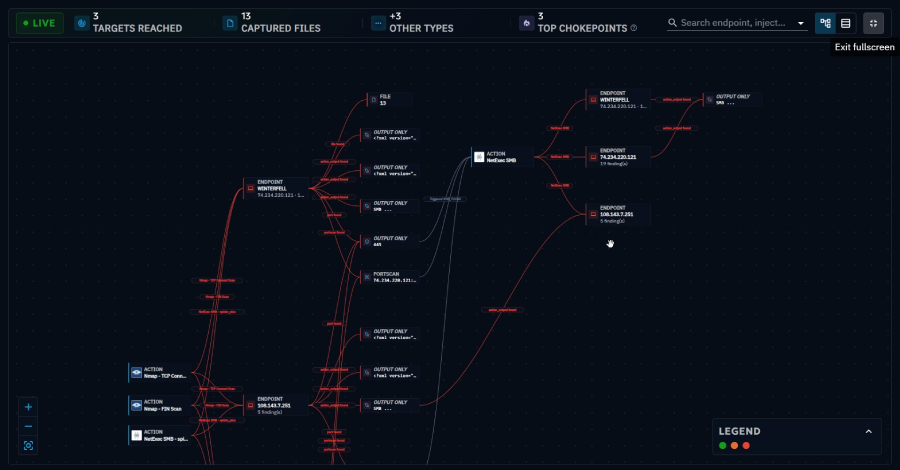
Attack Chains, Not Just Attack Surfaces: Why Testing Individual Techniques Misses the Point
Introduction Security teams have gotten pretty good at testing against what can hurt them. Can this EDR agent catch this...
 ENDPUNKTSICHERHEIT
RatHat Android Malware Abuses ADB to Retain Shell Access After Uninstall
Cybersecurity researchers have flagged a new Android malware called RatHat that's assessed to be operated by China-based threat actors and...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-27564: High Schwachstelle
A high-privileged remote attacker can exploit a command injection vulnerability in the /api/datastorage/data endpoint by sending a PUT request with...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-27563: High Schwachstelle
A high-privileged remote attacker can exploit a command injection vulnerability in the /api/datastorage/data endpoint by sending a crafted GET request...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-27562: High Schwachstelle
A high-privileged remote attacker can exploit a command injection vulnerability in the /api/iodd/config endpoint by sending a crafted PUT request...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-27561: High Schwachstelle
A high-privileged remote attacker can exploit a command injection vulnerability in the /api/iodd/config endpoint by sending a crafted GET request...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-27560: High Schwachstelle
A high-privileged remote attacker can exploit a command injection vulnerability in the /api/status/data endpoint by sending a crafted DELETE request...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-27557: High Schwachstelle
An unauthenticated remote attacker can exploit a path traversal vulnerability in the /index.php/view_uploaded_iodd_file endpoint allowing the SSH server's private keys...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-27552: High Schwachstelle
A low-privileged remote attacker can exploit improper authorization in the /index.php/attached_devices_tab/do_upload endpoint to upload IODD files to the device, potentially...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-84408: High Schwachstelle
QND contains an improper access control vulnerability in a named pipe, which may allow a local attacker who is logged...