Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-61628: High Schwachstelle
nginx ignition is a user interface for the nginx web server. Prior to version 2.41.1, `POST /api/users/onboarding/finish` is registered as...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-55071: High Schwachstelle
MCP-for-Stata is a MCP server for integrating Stata into agent loops with a safety-first design. Prior to version 1.19.0, the...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-84285: High Schwachstelle
An OS Command Injection vulnerability affecting Tuleap Enterprise Edition from 17.3 through 17.5 could allow an attacker to execute arbitrary...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-82187: Critical Schwachstelle
The Web to Print Online Designer WordPress plugin before 2.15.0 does not validate the type or extension of uploaded files,...
 ANWENDUNGSSICHERHEIT
Zyxel and Veeam Flaws Under Active Exploitation With Command and SYSTEM Access
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday added a now-patched security flaw impacting Zyxel GS1900 series switches...
 ANWENDUNGSSICHERHEIT
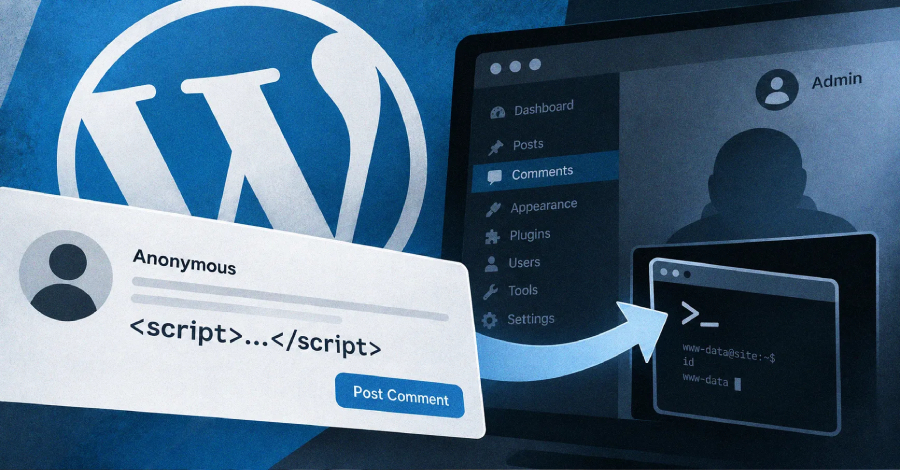
WordPress Comment2Shell Flaw Can Turn Anonymous Comment XSS Into RCE via Admin Session
A new flaw in WordPress core let an anonymous visitor leave a comment that planted a hidden script on the...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-93965: Medium Schwachstelle
A flaw has been found in aiyiyi121 SxDevOps 1.0/1.1. Affected is the function subprocess.Popen of the file backend/aiops/services.py of the...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-92541: High Schwachstelle
The Import and export users and customers WordPress plugin before 2.5.2 does not enforce the promote_users capability in its front-end...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-92540: High Schwachstelle
The Import and export users and customers WordPress plugin before 2.5.2 does not correctly enforce the promote_users capability when assigning...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-81650: High Schwachstelle
The Photo Gallery, Sliders, Proofing and WordPress plugin before 4.5.0 does not correctly validate the extensions of files extracted from...