Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-45048: High Schwachstelle
Open Access Management (OpenAM) is an access management solution. Prior to 16.1.1, SessionRequestHandler in the session management endpoint does not...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-57137: High Schwachstelle
PraisonAI is a multi-agent teams system. From 1.4.0 until 1.7.2, createAgentLoop() in src/praisonai-ts/src/ai/agent-loop.ts passes executable tools to generateText() before invoking...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-77853: High Schwachstelle
Improper neutralization of special elements used in an OS command ('OS Command Injection') issue exists in FF-RFI079I4 and FF-RFI078I4. A...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-90711: Critical Schwachstelle
proxy-addr is a Node.js module that determines a request's client address behind trusted reverse proxies, and it backs Express req.ip...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-57139: Critical Schwachstelle
PraisonAI is a multi-agent teams system. From 1.5.0 until 1.7.2, MCPServer.startHttp() in src/praisonai-ts/src/mcp/server.ts binds without a host restriction and forwards...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-57138: Critical Schwachstelle
PraisonAI is a multi-agent teams system. From 1.4.0 until 1.7.2, codeMode in src/praisonai-ts/src/tools/builtins/code-mode.ts executes untrusted JavaScript with new Function() inside...
 ANWENDUNGSSICHERHEIT
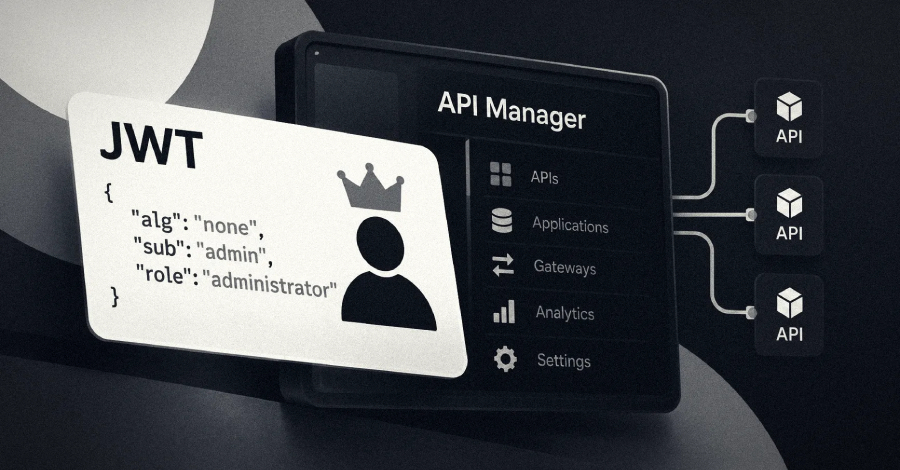
Active Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin Tokens
A critical security flaw in WSO2 API Manager has come under active exploitation in the wild, according to findings from...
 ANWENDUNGSSICHERHEIT
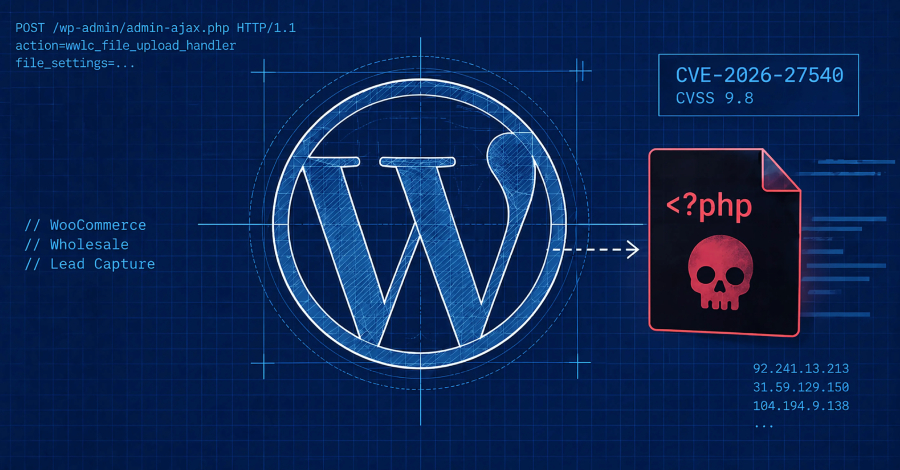
Attackers Exploit WooCommerce Wholesale Lead Capture Flaw to Plant PHP Web Shells
Threat actors are exploiting a critical security flaw in WooCommerce Wholesale Lead Capture, a premium WordPress plugin that has more...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-82773: Medium Schwachstelle
Cross-site scripting vulnerability exists in CONPROSYS M2M Gateway Series and CONPROSYS M2M Controller Series. If this vulnerability is exploited, an...
ANWENDUNGSSICHERHEIT
🟡 CVE-2023-51769: Medium Schwachstelle
Frappe before 14.49.0 allows an XSS attack that is associated with blog pages and exception pages.