Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-44190: High Schwachstelle
A flaw was found in the Ansible Lightspeed Visual Studio Code extension. This Command Injection vulnerability (CWE-78) allows a remote...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-44189: High Schwachstelle
A flaw was found in the Visual Studio Code Ansible Lightspeed extension's AnsiblePlaybookRunProvider. This command injection vulnerability allows an attacker...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-13185: High Schwachstelle
In Progress® Telerik® UI for AJAX prior to v2026.2.708, applications using cookie-based storage in RadPersistenceManager or RadDockLayout deserialize attacker-controlled cookie...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-65603: High Schwachstelle
The Grav Login plugin (grav-plugin-login) versions
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-14551: High Schwachstelle
The servereye client (also known as sensorhub, technically ClientAgentContainerService) versions 20.15 and earlier are vulnerable to Local Privilege Escalation. The...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-2395: Critical Schwachstelle
Improper neutralization of special elements used in an SQL command ('SQL injection') vulnerability in Xpoda Türkiye Informatics Technology Inc. No...
 ANWENDUNGSSICHERHEIT
AKTIV AUSGENUTZT – 🔴 CVE-2026-16232: Critical Luecke in Checkpoint Multi-Domain_Security_Management
An authentication bypass vulnerability in the Check Point SmartConsole login process allows an unauthenticated remote attacker to obtain an application...
 ANWENDUNGSSICHERHEIT
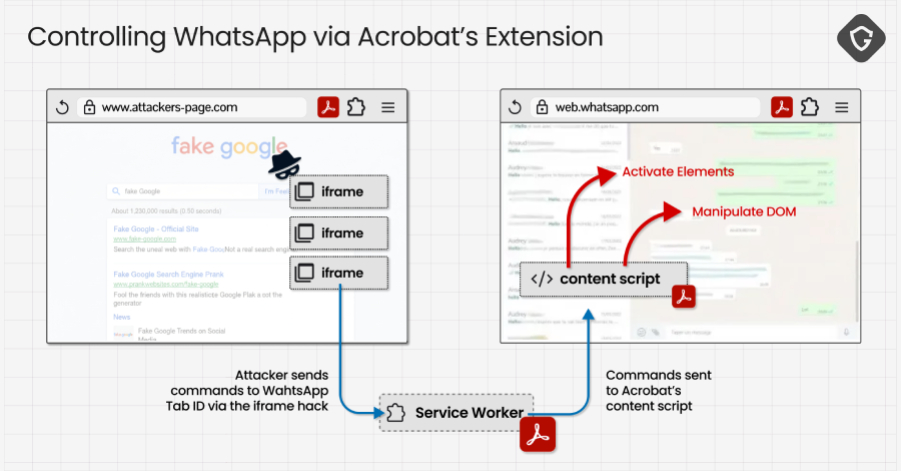
Adobe Acrobat Extension Flaw Let Malicious Sites Read WhatsApp Web Data
Cybersecurity researchers have disclosed details of a now-patched vulnerability chain in the Adobe Acrobat Chrome extension that has over 314...
 ANWENDUNGSSICHERHEIT
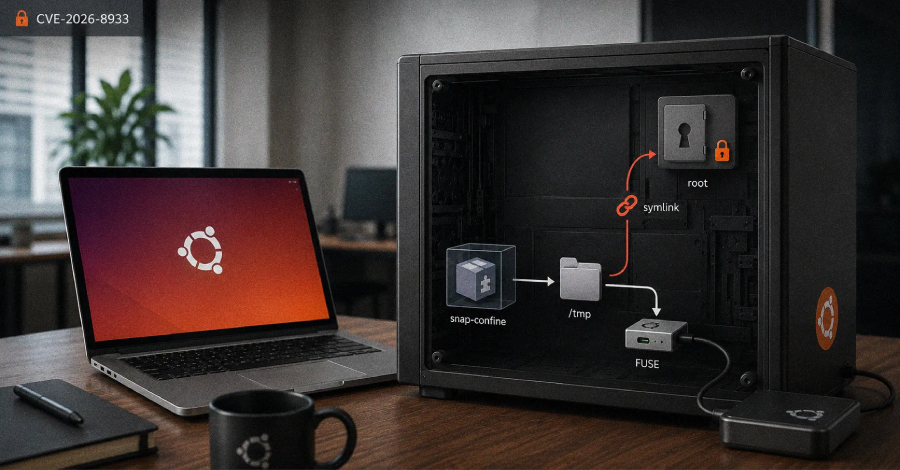
Ubuntu snap-confine Flaw Could Give Local Users Root on Default Desktop Installs
Cybersecurity researchers have disclosed details of a new local privilege escalation (LPE) vulnerability in snap-confine that an unprivileged user can...
ANWENDUNGSSICHERHEIT
🔴 CVE-2026-16396: Critical Schwachstelle
Privilege escalation in WebExtensions. This vulnerability was fixed in Firefox 153, Firefox ESR 140.13, Thunderbird 153, and Thunderbird 140.13.