Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-61436: High Schwachstelle
PraisonAI before 4.6.78 fails to verify Svix webhook signatures in AgentMail webhook mode, allowing unauthenticated attackers to forge message.received events....
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-12512: High Schwachstelle
The Quotes llama WordPress plugin before 3.1.6 does not properly sanitize and escape a user-supplied parameter before using it in...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-61457: High Schwachstelle
The Grav API plugin (getgrav/grav-plugin-api) before 1.0.3 contains a file upload extension bypass in the API media controller. HandlesMediaUploads::validateFileExtension() inspects...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-58655: High Schwachstelle
The bundled Grav Flex Objects plugin (getgrav/grav-plugin-flex-objects) before 1.4.0 contains a stored server-side template injection vulnerability. When rendering dynamic collection...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-35152: High Luecke in Apache Fineract
A SQL Injection vulnerability exists in Apache Fineract's Report Execution API (runreports endpoint) in versions up to and including 1.14.0....
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-15804: High Schwachstelle
The HCM developed by MetaGuru has a SQL Injection vulnerability. Authenticated remote attackers can inject SQL commands via specific parameters,...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-61736: Critical Schwachstelle
LightRAG provides simple and fast retrieval-augmented generation. Prior to 1.5.4, the server defaults to CORS_ORIGINS=* combined with allow_credentials=True in lightrag/api/lightrag_server.py,...
 ANWENDUNGSSICHERHEIT
SAP Patches CVSS 9.9 NetWeaver ABAP Flaw That Could Expose or Modify Data
SAP has rolled out updates to address multiple vulnerabilities as part of its July 2026 security updates, including a critical...
 ANWENDUNGSSICHERHEIT
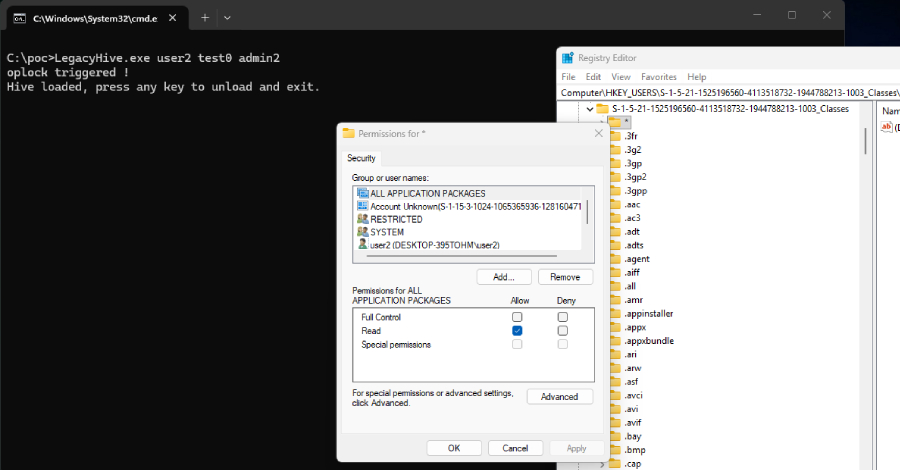
Researcher Drops New Windows Zero-Day PoC Hours After Microsoft Patch Tuesday
Security researcher Chaotic Eclipse (aka Nightmare-Eclipse) has released a new proof-of-concept (PoC) exploit called LegacyHive. It has been described as...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-15676: High Schwachstelle
A security flaw has been discovered in code-projects Online Job Portal up to 1.0. The impacted element is an unknown...