Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-14495: High Schwachstelle
The DoLogin Security plugin for WordPress is vulnerable to Authentication Bypass via Insufficient Randomness in all versions up to, and...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-54061: Critical Schwachstelle
Dgraph is an open source distributed GraphQL database. Prior to version 25.3.5, Dgraph Alpha exposes the RPCs used for external...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-58480: Critical Schwachstelle
Blocksy Companion Pro plugin for WordPress before 2.1.47 contains an unauthenticated arbitrary file upload vulnerability that allows attackers to upload...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-8307: Critical Schwachstelle
Improper neutralization of special elements used in an SQL command ('SQL injection') vulnerability in Webbeyaz Web Design Mediküm Web allows...
 ANWENDUNGSSICHERHEIT
Ubiquiti Patches Critical UniFi Flaws Across Connect, Talk, Access, Protect, and OS
Ubiquiti has shipped updates to address multiple critical security flaws impacting UniFi Connect, UniFi Talk, UniFi Access, UniFi Protect, and...
 ANWENDUNGSSICHERHEIT
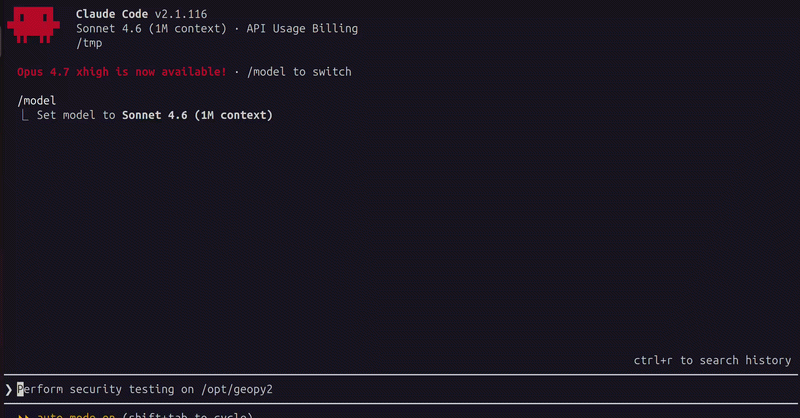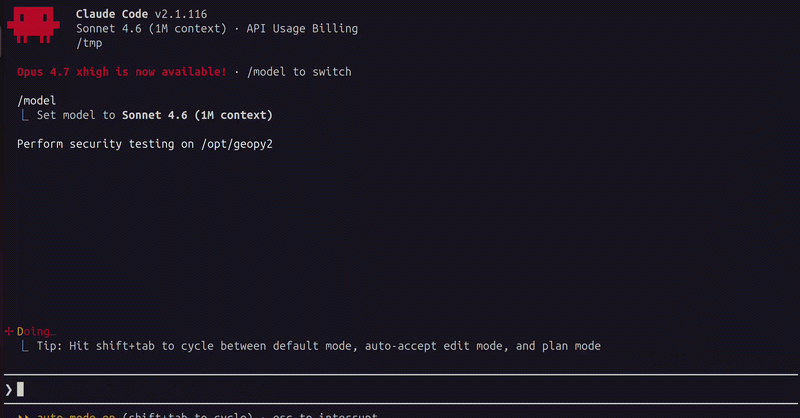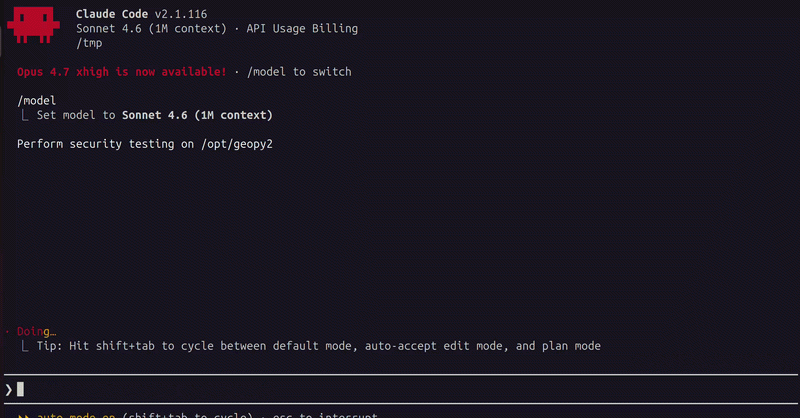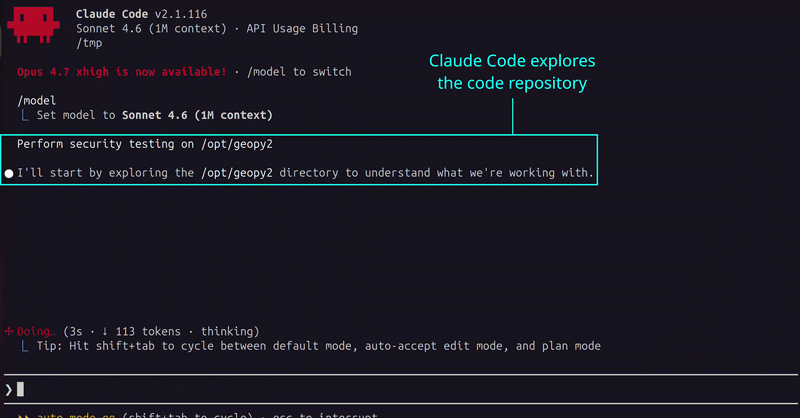
Top AI Agents Built to Catch Malicious Code Can Be Tricked Into Running It
Ask an AI coding agent to scan open-source code for security holes, and it might run the attacker's code on...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-14904: Medium Schwachstelle
AWS Research and Engineering Studio (RES) is an open-source solution that enables researchers and engineers to create and manage secure...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2025-12799: Medium Schwachstelle
A flaw was found in Jastow. Jastow is vulnerable to Cross-Site Scripting (XSS) attack. If using a set of combined...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-49296: Medium Luecke in Apache Airflow
Before apache-airflow 3.3.0, a user authorized to read one Dag could disclose the source of other Dags co-located in the...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-53935: Medium Schwachstelle
Cilium is a networking, observability, and security solution. Prior to 1.17.16, from 1.18.2 to 1.18.9, and from 1.19.0 to 1.19.3,...