Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-77547: Critical Schwachstelle
A malicious actor with access to the network and low privileges could exploit an Improper Input Validation vulnerability found in...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-77546: Critical Schwachstelle
A malicious actor with access to the network and low privileges could exploit an Improper Input Validation vulnerability found in...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-77543: Critical Schwachstelle
A malicious actor with access to the network and low privileges could exploit an Improper Input Validation vulnerability found in...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-77533: Critical Schwachstelle
A malicious actor with access to the network and low privileges could exploit an Improper Input Validation vulnerability found in...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-77554: Critical Schwachstelle
A malicious actor with access to the network could exploit an Improper Input Validation vulnerability found in UniFi Talk Application...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-77537: Critical Schwachstelle
A malicious actor with access to the network could exploit an Improper Input Validation vulnerability found in UniFi Protect Application...
 ANWENDUNGSSICHERHEIT
Claude Opus 4.6 Bypasses Gym Booking Limit, Cancels Other Users‘ Reservations in Tests
Aikido Security has published research that recreates the Australian gym-booking incident in a synthetic environment, finding that Claude Opus 4.6,...
 ANWENDUNGSSICHERHEIT
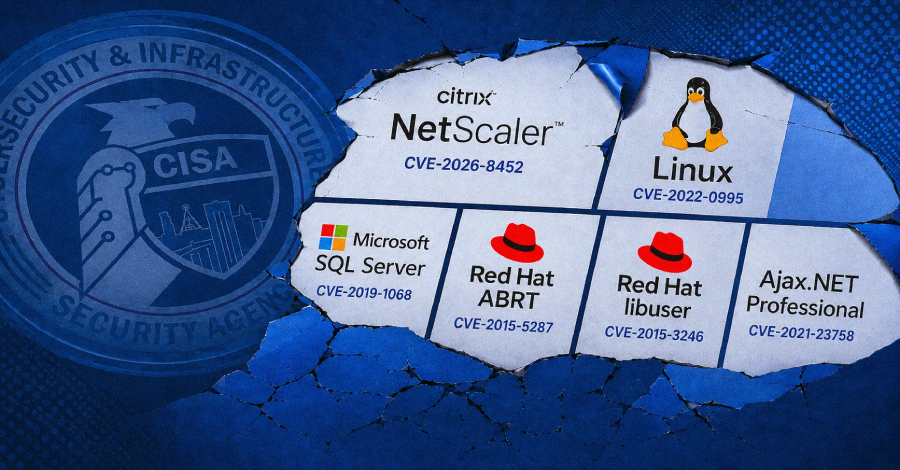
CISA Adds Six Exploited Flaws to KEV, Including NetScaler, Linux, and SQL Server Bugs
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added six flaws to its Known Exploited Vulnerabilities (KEV) catalog,...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-78470: Medium Schwachstelle
The WP Project Manager Pro plugin for WordPress is vulnerable to SQL Injection in all versions up to, and including,...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-75971: High Schwachstelle
The ShopEngine Elementor WooCommerce Builder Addon – All in One WooCommerce Solution plugin for WordPress is vulnerable to Privilege Escalation...