Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-49845: Critical Schwachstelle
SQL injection in Hive Metastore direct SQL partition-name resolution in Apache Hive before 4.2.1 on all platforms allows authenticated users...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-78568: Critical Schwachstelle
The Total Donations plugin for WordPress is vulnerable to SQL Injection in all versions up to, and including, 2.0.5 due...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-63586: Critical Schwachstelle
The web-based management interface uses a modified uhttpd server with CGI shell scripts. The HTTP Basic Authentication username, taken directly...
 ANWENDUNGSSICHERHEIT
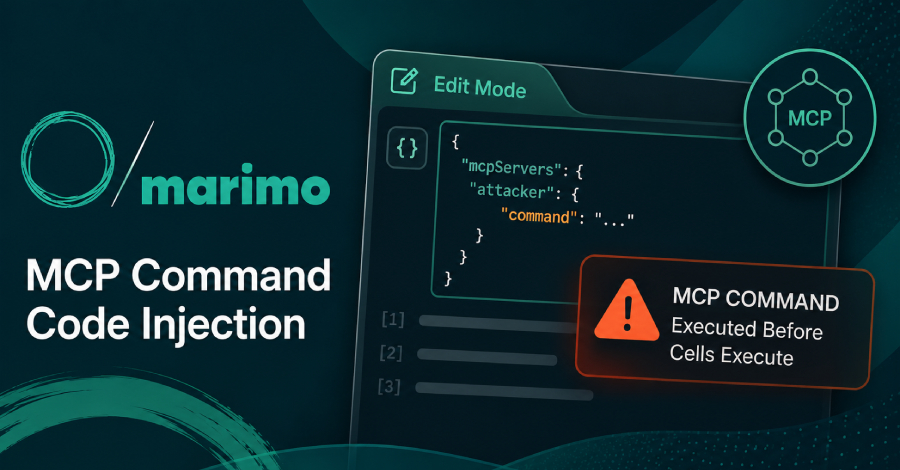
Marimo Notebook Flaw Could Run MCP Commands Before Cells Execute in Edit Mode
Marimo has addressed a high-severity security flaw in its notebook software that allowed an attacker to execute an attacker-supplied Model...
 ANWENDUNGSSICHERHEIT
Critical Gitea RCE Actively Exploited as Reported Attack Drops Miner-Like Payload
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday warned of active exploitation efforts targeting a recently patched critical...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-78248: High Schwachstelle
A vulnerability was determined in SourceCodester Simple Online Food Ordering System 1.0. Impacted is an unknown function of the file...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-78247: High Schwachstelle
A vulnerability was found in SourceCodester Simple Online Food Ordering System 1.0. This issue affects some unknown processing of the...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-78246: High Schwachstelle
A vulnerability has been found in itsourcecode Online Clinic Management System 1.0. This vulnerability affects unknown code of the file...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-78245: High Schwachstelle
A flaw has been found in itsourcecode Online Pharmacy System 1.0. This affects the function move_uploaded_file of the file all_users/register.php...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-78244: High Schwachstelle
A vulnerability was detected in itsourcecode Real Estate Management System 1.0. Affected by this issue is some unknown functionality of...