Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-12576: High Schwachstelle
DVP80ES3 with Improper Enforcement of Message Integrity During Transmission in a Communication Channel vulnerability.
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-12575: High Schwachstelle
DVP80ES3 with Improper Resource Shutdown or Release vulnerability.
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-11823: High Schwachstelle
The BookingPress Appointment Booking Pro plugin for WordPress is vulnerable to SQL Injection via the 'store_service_date' parameter of the bpa_assign_staffmember_to_slots()...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-11568: High Schwachstelle
The Product Configurator for WooCommerce WordPress plugin before 1.7.3 does not perform any authorisation or post-status check before returning WooCommerce...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-23537: Critical Schwachstelle
A vulnerability has been identified in the Feast Feature Server’s `/save-document` endpoint that allows an unauthenticated remote attacker to write...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-14198: Critical Luecke in Fastify Fastify\/Middie
@fastify/middie versions 9.1.0 through 9.3.2 decode the encoded slash %2F inside path parameter values before matching middleware paths, while Fastify's...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-57692: Critical Schwachstelle
Incorrect Privilege Assignment vulnerability in LCweb PrivateContent allows Privilege Escalation. This issue affects PrivateContent: from n/a through 9.9.2.
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-11387: Critical Schwachstelle
The SMS Alert – SMS & OTP for WooCommerce, Order Notifications & Abandoned Cart Recovery plugin for WordPress is vulnerable...
 ANWENDUNGSSICHERHEIT
SharePoint RCE CVE-2026-45659 Added to CISA KEV After Active Exploitation
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a high-severity flaw impacting Microsoft SharePoint Server to its...
 ANWENDUNGSSICHERHEIT
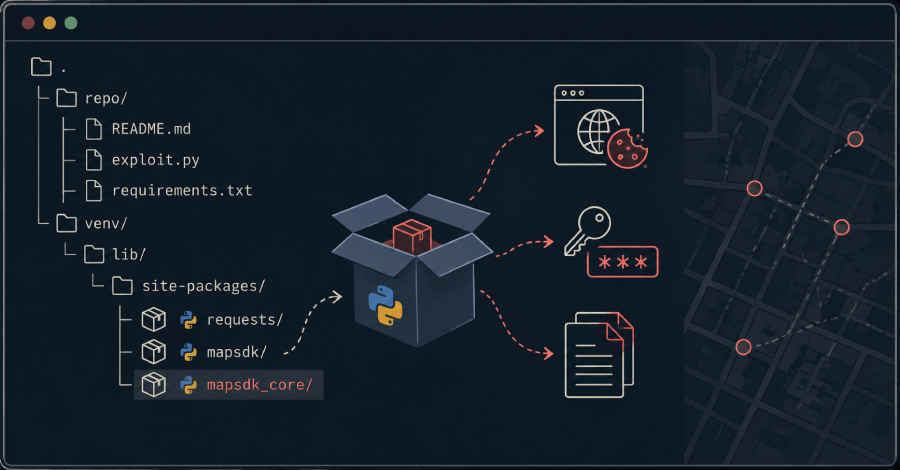
New ChocoPoC RAT Targets Vulnerability Researchers via Fake PoC Exploit Repos
Attackers are hiding a data-stealing trojan inside fake exploit code aimed at the people who hunt bugs for a living....