Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-56028: Critical Schwachstelle
Unauthenticated Privilege Escalation in Easy Elements for Elementor – Addons & Website Templates
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-57878: Critical Schwachstelle
An unauthenticated stack-based buffer overflow vulnerability exists in thttpd in GeoVision GV-LPC2011 and GV-LPC2211 V1.12 and earlier. The vulnerability is...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-56027: Critical Schwachstelle
Customer Arbitrary File Upload in Booster for WooCommerce
 ANWENDUNGSSICHERHEIT
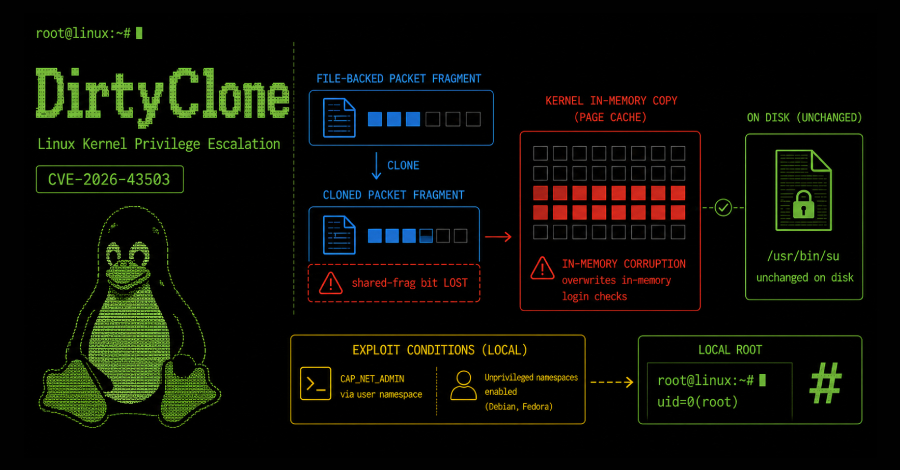
New DirtyClone Linux Kernel Flaw Lets Local Users Gain Root via Cloned Packets
DirtyClone is a new Linux kernel privilege escalation in the DirtyFrag family. JFrog Security Research published a working exploit walkthrough for the...
 ANWENDUNGSSICHERHEIT
CISA Adds Exploited PTC Windchill RCE Flaw to KEV as Web Shell Attacks Continue
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added a critical remote code execution vulnerability impacting PTC Windchill...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-12937: High Schwachstelle
The Tourfic – AI Powered Travel Booking, Hotel Booking & Car Rental WordPress Plugin plugin for WordPress is vulnerable to...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-9702: High Schwachstelle
The InPost PL WordPress plugin before 1.9.1 does not verify that the request originates from the legitimate buyer before allowing...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-5305: High Schwachstelle
The Email Address Encoder WordPress plugin before 1.0.25, email-encoder-premium WordPress plugin before 0.3.12 does not properly handle email replacement, which...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-12244: High Luecke in Nlnetlabs Nsd
If NSD is configured as secondary for a zone, the primary of that zone can crash NSD with an AXFR...
 ANWENDUNGSSICHERHEIT
Cordyceps CI/CD Flaws Expose 300+ GitHub Repositories to Supply-Chain Attacks
Cybersecurity researchers have flagged a new class of CI/CD workflow weakness that allows attackers to hijack workflows and compromise open-source...