Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-56052: High Schwachstelle
Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in FunnelKit Funnel Builder by FunnelKit allows...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-9710: High Schwachstelle
The Cornerstone WordPress plugin before 7.8.8 does not enforce capability checks on one of its CSS-preview request handlers, and exposes...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-9709: High Schwachstelle
The Cornerstone WordPress plugin before 7.8.9 does not enforce capability checks on one of its REST API routes, allowing any...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-56245: High Schwachstelle
Supabase Capgo before 12.128.2 contains an authorization bypass vulnerability in the SECURITY DEFINER record_build_time RPC function that allows unauthenticated attackers...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-56232: High Schwachstelle
Capgo before 12.128.2 fails to enforce limited_to_orgs and limited_to_apps constraints on subkeys provided via x-limited-key-id header in middlewareKey function. Attackers...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-12242: High Schwachstelle
The AdRotate Banner Manager plugin for WordPress is vulnerable to PHP Code Injection in all versions up to, and including,...
 ANWENDUNGSSICHERHEIT
CISA Warns Critical Lantronix EDS5000 Flaw Is Being Actively Exploited
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday warned of active exploitation of a critical security flaw impacting...
 ANWENDUNGSSICHERHEIT
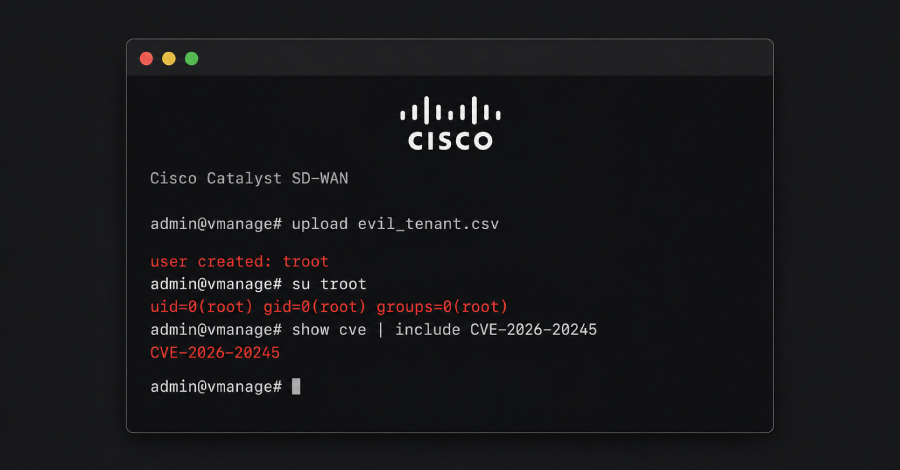
Cisco Catalyst SD-WAN Zero-Day CVE-2026-20245 Exploited to Gain Root Access
An unknown threat actor exploited a recently disclosed high-severity security flaw impacting Cisco Catalyst SD-WAN as a zero-day at least...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-13007: High Schwachstelle
Tenable Identity Exposure contains multiple unauthenticated API endpoints under /w/api/* that expose sensitive application configuration data including cleartext LDAP credentials,...
ANWENDUNGSSICHERHEIT
🟠 CVE-2025-61025: High Schwachstelle
An issue in the sslr_qst_get component of openlink virtuoso-opensource v7.2.11 allows attackers to cause a Denial of Service (DoS) via...