Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
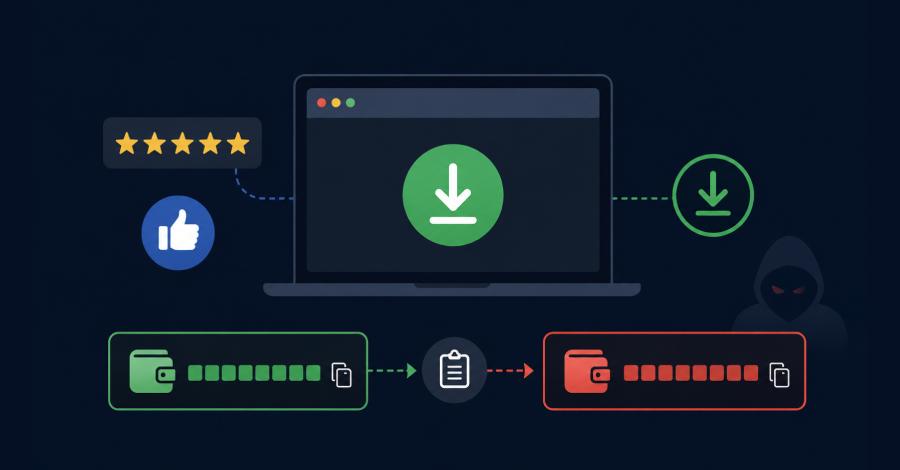
Crypto Clipper Campaign Abuses Fake Reviews, AI Narrators, and VirusTotal Comments
An unknown threat actor has been observed leveraging paid or promoted posts on legitimate news websites to drum up buzz...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-54198: High Schwachstelle
Unauthenticated Cross Site Scripting (XSS) in Media LIbrary Assistant
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-54191: High Schwachstelle
Unauthenticated Cross Site Scripting (XSS) in Pods
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-39437: High Schwachstelle
Unauthenticated Cross Site Scripting (XSS) in Min Max Step Quantity Limits Manager for WooCommerce
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-12324: High Luecke in Mozilla Firefox
Incorrect boundary conditions in the Graphics: CanvasWebGL component. This vulnerability was fixed in Firefox 152, Firefox ESR 140.12, Thunderbird 152,...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-12398: High Schwachstelle
A command injection vulnerability was found in galaxy_ng. The do_git_checkout() function in the legacy role import API (v1) interpolates unsanitized...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-52711: High Schwachstelle
Unauthenticated Broken Access Control in WooCommerce POS
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-52712: High Schwachstelle
Subscriber SQL Injection in Attendance Manager
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-47684: High Schwachstelle
Sync-in Server is a secure, open-source platform for file storage, sharing, collaboration, and syncing. Prior to version 2.3.0, the private...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-48780: High Schwachstelle
Forem is open source software for building communities. Prior to commit a2ab6d4, a maliciously crafted email address could allow an...