Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-40750: Critical Schwachstelle
Unrestricted Upload of File with Dangerous Type vulnerability in themagnifico52 Kids Online Store allows Upload a Web Shell to a...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-49774: Critical Schwachstelle
Improper Control of Generation of Code ('Code Injection') vulnerability in Filipe Nasc RD Station allows Remote Code Inclusion. This issue...
 ANWENDUNGSSICHERHEIT
CISA Warns of Actively Exploited Joomla JCE Flaw Allowing PHP Code Execution
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added a maximum-severity security flaw impacting Widget Factory Joomla Content...
 ANWENDUNGSSICHERHEIT
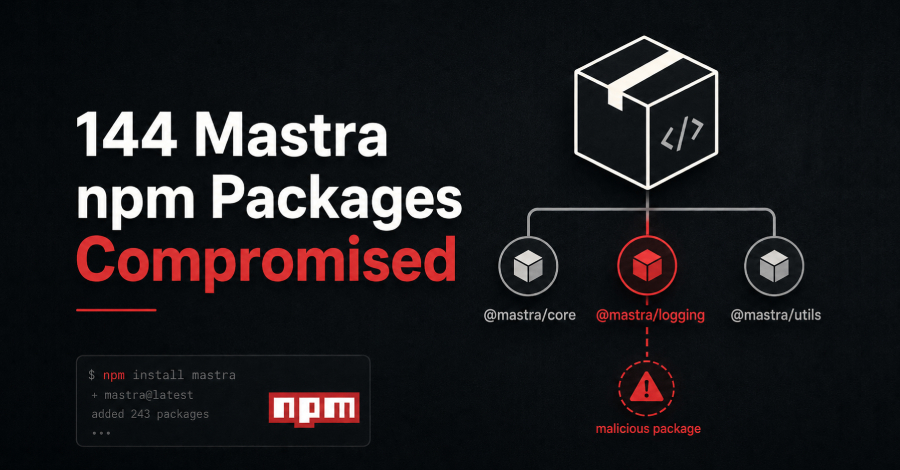
144 Mastra npm Packages Compromised via Hijacked Contributor Account
As many as 144 npm packages associated with the Mastra namespace ("@mastra/*"), a popular open-source JavaScript and TypeScript framework for...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-9595: Medium Luecke in Webpack.Js Webpack-Dev-Server
Impact: When a user-configured proxy on webpack-dev-server has a broad context (e.g. /) and ws: true, it also intercepts the...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-5038: Medium Luecke in Expressjs Multer
Impact: multer versions 2.0.0-alpha.1 through 2.1.1 and 3.0.0-alpha.1 are vulnerable to a Denial of Service when using diskStorage. Aborted or...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2016-20083: Medium Schwachstelle
WordPress More Fields Plugin 2.1 contains a cross-site request forgery vulnerability that allows attackers to perform unauthorized actions by disabling...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-44188: Medium Schwachstelle
A flaw was found in Ansible Lightspeed. This vulnerability, related to insufficient session expiration, allows a remote attacker to maintain...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-8385: Medium Schwachstelle
The WP Go Maps WordPress plugin before 10.0.10 does not properly enforce the marker approval filter on the admin-ajax fallback...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-11931: Medium Schwachstelle
Incorrect default permissions in Kiro IDE on macOS and Linux before version 0.11.133 could expose the authentication token cache file...