Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-57308: Critical Schwachstelle
Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Apache Syncope. An administrator with adequate...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-53421: Critical Schwachstelle
Improper Isolation or Compartmentalization vulnerability in Apache Syncope. An administrator with adequate entitlements can achieve remote code execution through the...
 ANWENDUNGSSICHERHEIT
⚡ Weekly Recap: WordPress RCE, SonicWall 0-Days, AI Service Attacks, SharePoint 0-Day and More
A single request should not be able to do this much. But this week, small inputs led to code execution,...
 ANWENDUNGSSICHERHEIT
Critical ServiceNow AI Platform Flaw Exploited for Unauthenticated Code Execution
Threat actors are now exploiting a recently disclosed critical security flaw impacting ServiceNow AI Platform, according to Defused Cyber. In...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-63809: High Schwachstelle
In the Linux kernel, the following vulnerability has been resolved: bpf: use kvfree() for replaced sysctl write buffer proc_sys_call_handler() allocates...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-53390: High Schwachstelle
In the Linux kernel, the following vulnerability has been resolved: ksmbd: fix out-of-bounds read in smb_check_perm_dacl() The permission-check ACE walk...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-63831: High Schwachstelle
In the Linux kernel, the following vulnerability has been resolved: mac802154: llsec: add skb_cow_data() before in-place crypto llsec_do_encrypt_unauth(), llsec_do_encrypt_auth(), llsec_do_decrypt_u...
 ANWENDUNGSSICHERHEIT
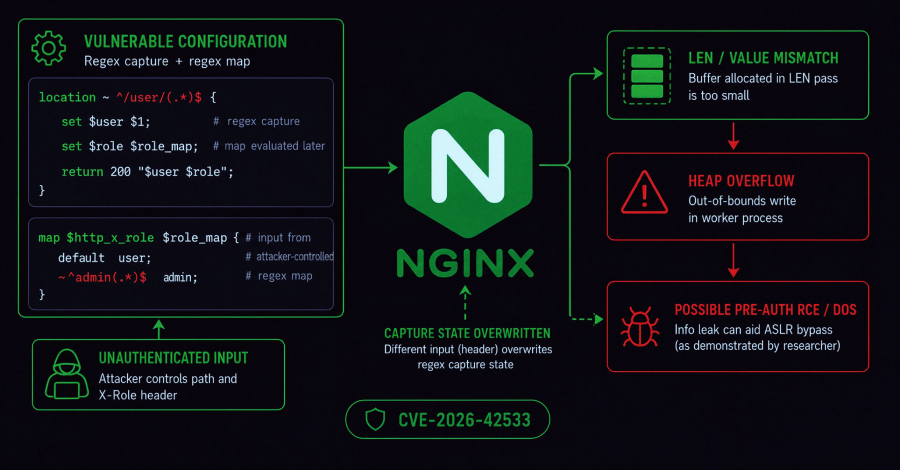
Critical NGINX Vulnerability Can Crash Workers and May Allow Remote Code Execution
F5 has shipped fixes for a critical nginx flaw that lets a remote, unauthenticated attacker trigger a heap buffer overflow...
 ANWENDUNGSSICHERHEIT
World’s Largest AI Model Repository Hugging Face Breached by Autonomous AI Agent
In an ironic twist, open-source artificial intelligence (AI) platform Hugging Face revealed that it was the victim of a hack...
ANWENDUNGSSICHERHEIT
🟡 CVE-2024-58370: Medium Schwachstelle
SurrealDB versions before 1.1.0 fail to enforce recursion depth limits when parsing nested SurrealQL statements including IF, RELATE, and attribute...