Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-49471: High Schwachstelle
Serena is a powerful MCP toolkit for coding that provides semantic retrieval and editing capabilities. Prior to v1.5.2, Serena's built-in...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-12277: High Schwachstelle
The Frontend File Manager Plugin WordPress plugin through 23.6 does not validate a file path derived from user input before...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-23697: High Schwachstelle
Vtiger CRM before 8.4.0 contains an authenticated file upload vulnerability that allows low-privileged users to achieve remote code execution by...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-44938: High Schwachstelle
A vulnerability has been identified in Fleet's agent-side deployer, which did not filter security-sensitive keys from namespaceLabels in fleet.yaml (or...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-13696: High Schwachstelle
Improper neutralization of special elements used in an LDAP query ('LDAP injection') vulnerability in HAVELSAN Inc. Liman MYS allows LDAP...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-4375: Critical Schwachstelle
The DoLeads Integrator WordPress plugin through 0.65, wp2epub WordPress plugin through 0.65 have been seen to be used to achieve...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-59800: Critical Schwachstelle
9Router before 0.4.44 contains an OS command injection vulnerability in the unauthenticated POST /api/tunnel/tailscale-install endpoint (this route is not covered...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-14345: Critical Schwachstelle
The WPFunnels – Funnel Builder for WooCommerce with Checkout & One Click Upsell plugin for WordPress is vulnerable to Remote...
 ANWENDUNGSSICHERHEIT
Writer AI Flaw Could Let Agent Previews Leak Session Tokens Across Tenants
Cybersecurity researchers have disclosed details of a now-patched critical session isolation vulnerability in Writer, an enterprise generative artificial intelligence (AI)...
 ANWENDUNGSSICHERHEIT
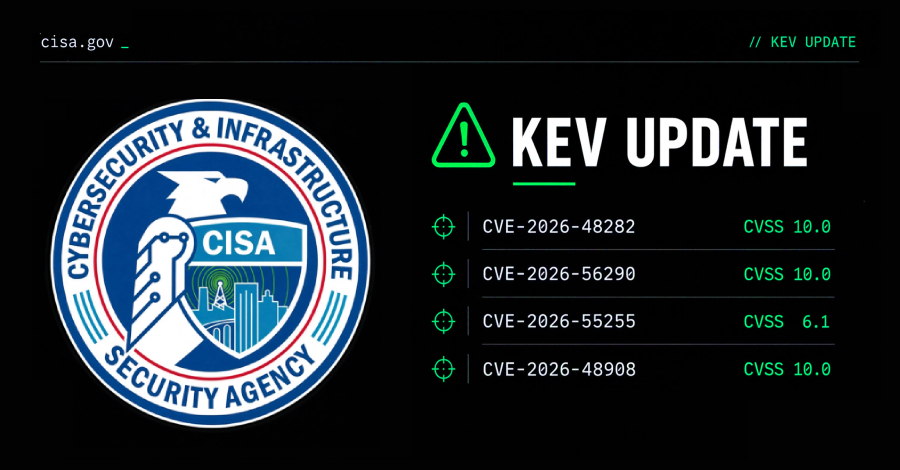
CISA Adds 4 Actively Exploited Adobe, Joomla, and Langflow Flaws to KEV
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added four security flaws to its Known Exploited Vulnerabilities (KEV)...