Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-40047: Critical Schwachstelle
Improper Neutralization of Argument Delimiters in a Command ('Argument Injection') vulnerability in Apache Camel Docling component. The camel-docling component invokes...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-48204: Critical Luecke in Apache Camel
Improper Input Validation, Improper Access Control vulnerability in Apache Camel in Camel Mongodb Gridfs component. The camel-mongodb-gridfs producer selects the...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-46456: Critical Luecke in Apache Camel
Improper Input Validation vulnerability in Apache Camel AWS2-SQS Component. The camel-aws2-sqs component map inbound message attributes into the Camel Exchange...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-46455: Critical Luecke in Apache Camel
Insufficient Session Expiration vulnerability in Apache Camel Keycloak Component. The camel-keycloak security helper KeycloakSecurityHelper.parseAndVerifyAccessToken builds a Keycloak TokenVerifier u...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-43867: Critical Luecke in Apache Camel
Deserialization of Untrusted Data vulnerability in Apache Camel PQC Component. The camel-pqc component persists post-quantum key metadata (KeyMetadata) through pluggable...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-40141: Critical Luecke in Beyondtrust Remote_Support
A high-severity vulnerability exists in a web application component of BeyondTrust Remote Support and Privileged Remote Access related to the...
 ANWENDUNGSSICHERHEIT
Threat Actors Probe Gitea Docker Flaw CVE-2026-20896 13 Days After Disclosure
Threat actors have been observed attempting to exploit a recently patched critical security flaw in Gitea Docker images, according to...
 ANWENDUNGSSICHERHEIT
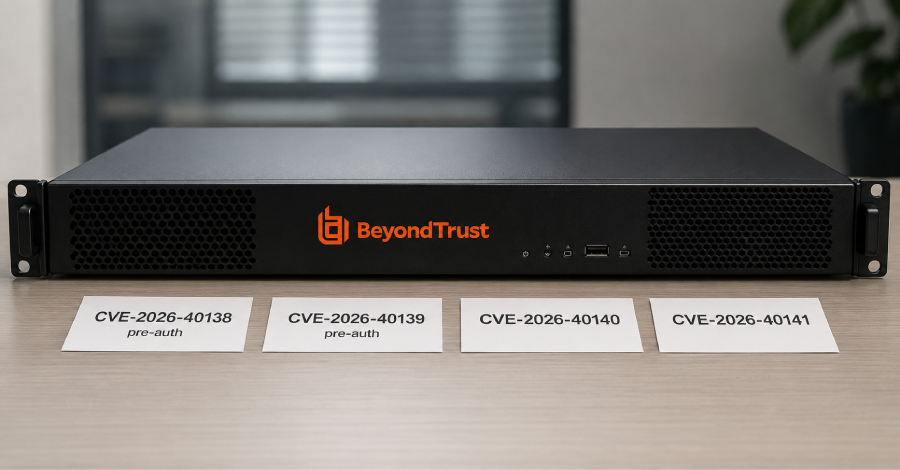
BeyondTrust Patches Critical Auth Bypass Flaws in Remote Support and PRA
BeyondTrust has released updates to address two critical security flaws affecting Remote Support (RS) and Privileged Remote Access (PRA) products...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-14767: Medium Schwachstelle
A security flaw has been discovered in CodeAstro Ecommerce Website 1.0. This affects an unknown part of the file /ecommerce-website-php/customer/confirm.php...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-14766: Medium Schwachstelle
A vulnerability was identified in CodeAstro Apartment Visitor Management System 1.0. Affected by this issue is some unknown functionality of...