Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-85184: Critical Schwachstelle
@fastify/middie versions >= 9.1.0 and before 9.3.4 decide whether to run path-scoped middleware by matching against the raw request target,...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-85085: Critical Schwachstelle
The Canva Android App before 2.376.0 allowed an external origin to be loaded in a privileged WebView. A threat actor...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-82923: Critical Schwachstelle
The AI Website Builder WordPress plugin (GitHub build) 1.0.0 does not perform any authorisation or nonce check on its REST...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-62928: Critical Schwachstelle
XING CPTrans-ME-X contains an OS Command Injection (CWE-78). Unauthenticated OS command may be injected.
 ANWENDUNGSSICHERHEIT
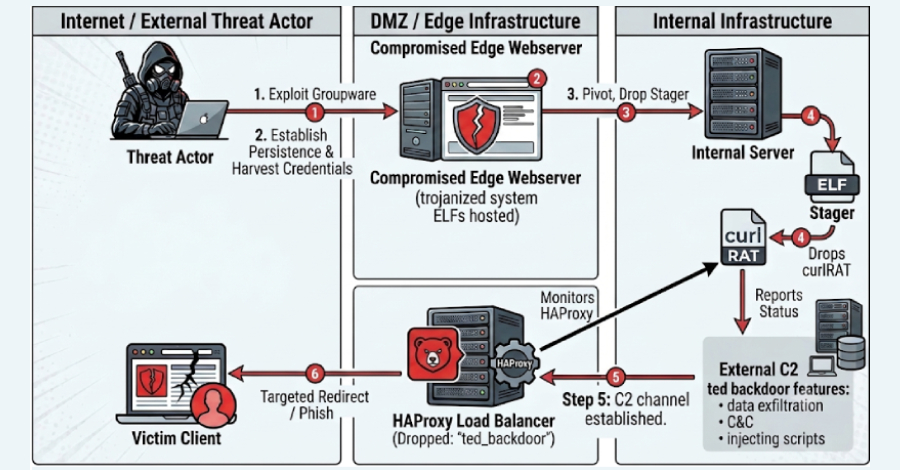
New Ted Backdoor Hides Inside Victims‘ Own HAProxy Builds to Intercept Web Traffic
A previously undocumented Linux toolkit has been found compiled directly into the trojanized HAProxy load balancers of two South Korean...
 ANWENDUNGSSICHERHEIT
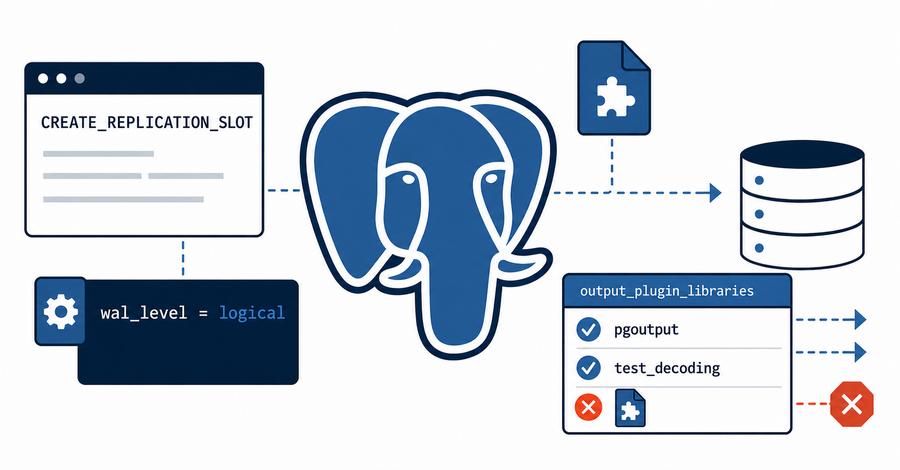
PostgreSQL Fixes 12-Year-Old Logical Decoding Flaw Enabling Replication-Role Code Execution
PostgreSQL has released updates to address a security flaw that allows an account with the REPLICATION attribute to run arbitrary...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2021-43614: Medium Schwachstelle
Error in handling the PlatformLangCodes UEFI variable could cause a buffer overflow, leading to resource exhaustion and failure.
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-85164: High Schwachstelle
WWBN AVideo through commit c91b5975d contains a server-side request forgery vulnerability in the set_api_userImages API endpoint that fails to validate...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-80749: High Schwachstelle
In the Linux kernel, the following vulnerability has been resolved: drm/connector/hdmi: Fix out of bounds memory read A helper function...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-85155: High Schwachstelle
WWBN AVideo contains a SQL injection vulnerability in the sort column parameter of the get.json.php endpoint with APIName=channels that allows...