Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-116878: High Schwachstelle
Semantic MediaWiki from 2.5.0 before 7.3.1 contains an uncontrolled resource consumption vulnerability that allows anonymous attackers to force quadratic computation...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-18449: High Schwachstelle
The BMC does not correctly enforce integrity and encryption requirements for IPMI commands. An attacker may be able to craft...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-75891: High Schwachstelle
The Kirki plugin for WordPress is vulnerable to Privilege Escalation via PHP Object Injection in all versions up to, and...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-117532: Critical Schwachstelle
REDAXO core from 5.3.0 before 5.21.4 contains an authentication bypass vulnerability in the structure/history plugin that allows unauthenticated attackers to...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-82119: Critical Schwachstelle
OS Command Injection Vulnerability in HiRDB. This issue affects HiRDB Server Version 10: from 10-00 before 10-12-01; HiRDB Server Version...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-18450: Critical Schwachstelle
The BMC does not correctly enforce integrity and encryption requirements for IPMI commands. An attacker may be able to craft...
 ANWENDUNGSSICHERHEIT
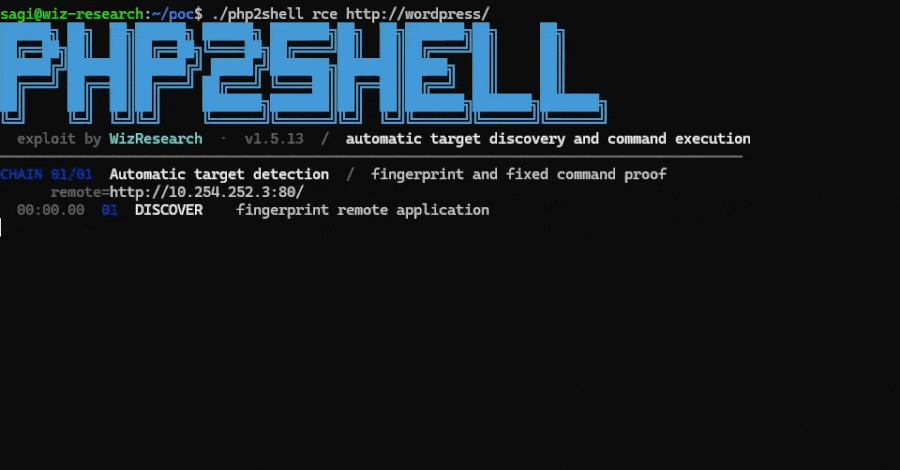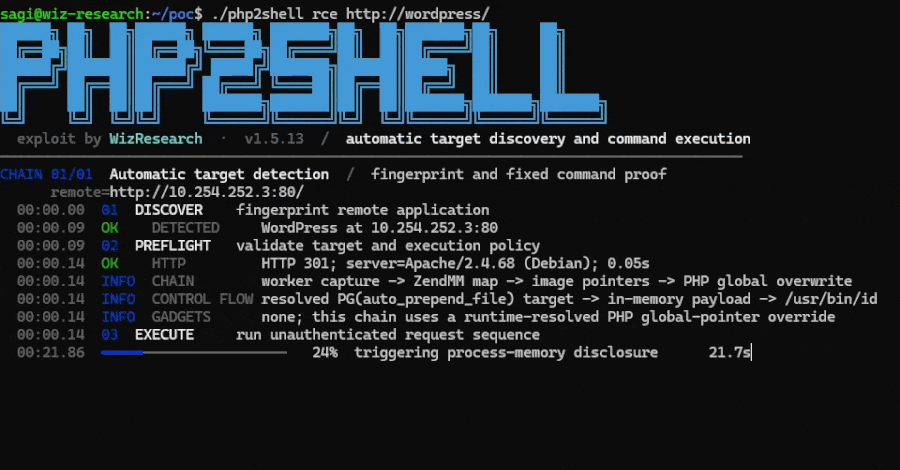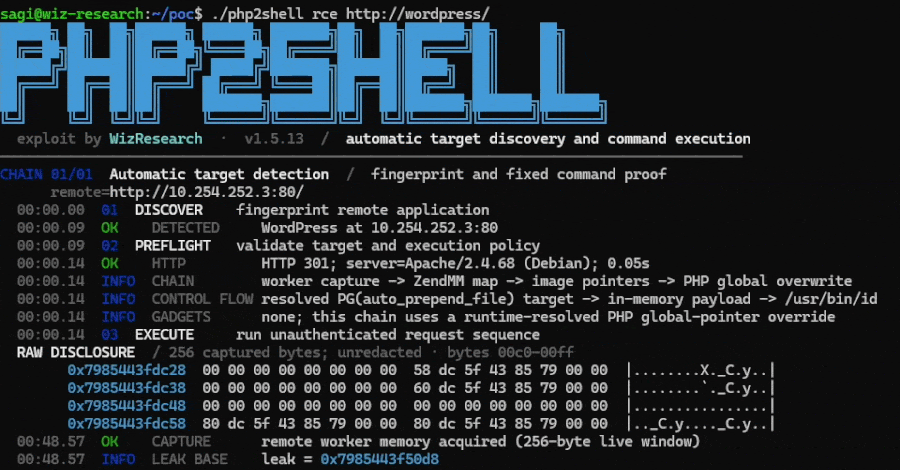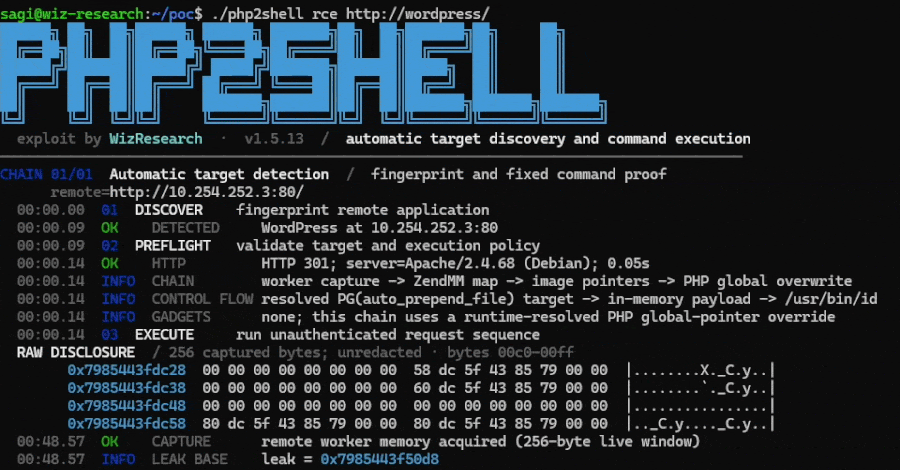
PHP Issues Emergency Patches for Two Critical PHP2Shell RCE Flaws as Exploit Attempts Emerge
PHP has released emergency updates that fix two critical flaws in the language itself, letting an attacker without an account...
 ANWENDUNGSSICHERHEIT
Critical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of Releases
GitLab released fixes on October 21 for a flaw that lets an attacker run code on a self-managed server without...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-113385: Medium Schwachstelle
A vulnerability has been found in LeeDrOiD Labs Shortcutter 2 App 9.0.48 on Android. This issue affects the function Class.forName...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-113378: Medium Schwachstelle
A security flaw has been discovered in mcollina mcp-ripgrep up to 0.4.0. Affected is an unknown function of the file...