Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-105311: High Schwachstelle
The StreamsHub Console operator acts as a confused deputy: a Kubernetes tenant with permission to create a Console custom resource...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-113407: High Schwachstelle
BA-Workflow developed by YS-infoware has a SQL Injection vulnerability. Authenticated remote attackers can inject arbitrary SQL statements to read, modify,...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-113406: High Schwachstelle
BA-Workflow developed by YS-infoware has a SQL Injection vulnerability. Authenticated remote attackers can inject arbitrary SQL statements to read, modify,...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-113405: High Schwachstelle
BA-Workflow developed by YS-infoware has a SQL Injection vulnerability. Authenticated remote attackers can inject arbitrary SQL statements to read, modify,...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-113404: High Schwachstelle
WebITR developed by Uniong has a Insecure Deserialization vulnerability. Authenticated remote attackers can use the hard-coded cryptographic key to craft...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-105312: Critical Schwachstelle
A Kubernetes tenant with create permission on Console custom resources can set spec.containers.api.spec.image to an arbitrary container image. The operator...
 ANWENDUNGSSICHERHEIT
PHP2Shell: Two Unpatched Critical PHP RCE Flaws (CVSS 9.2) Trigger Emergency Security Alert
This story is developing and was written before PHP's scheduled 14:00 UTC release on October 21. Once the release is...
 ANWENDUNGSSICHERHEIT
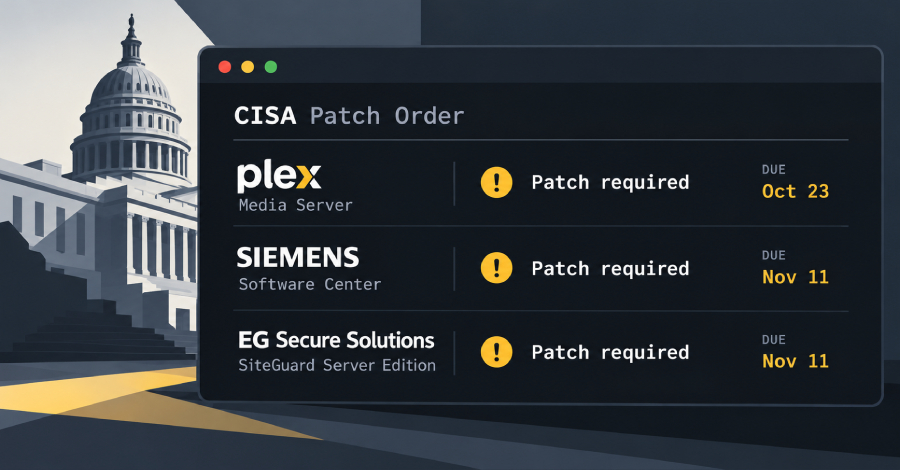
CISA Orders Federal Agencies to Patch Exploited Plex2Shell, Siemens, and SiteGuard Flaws
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added four vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog,...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-106028: Medium Schwachstelle
The ActiveTrail for WooCommerce WordPress plugin through 1.2.6 does not perform any authorization check before creating WooCommerce coupons, allowing unauthenticated...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-112100: Medium Schwachstelle
A vulnerability was determined in DeepPavlov up to 1.7.0. This affects the function MultiTaskPipelinePreprocessor.__init__ of the file deeppavlov/models/preprocessors/multitask_preprocessor.py. This m...