Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-78286: Critical Schwachstelle
Unauthenticated PHP Object Injection in Geo Controller
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-47892: Critical Schwachstelle
A WebFlux application using functional endpoints and deployed with DispatcherServlet may be vulnerable to a header predicate bypass in a...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-47891: Critical Schwachstelle
A Spring WebFlux application that relies on the Aalto XML processor to parse XML input does not correctly enforce the...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-47890: Critical Schwachstelle
Spring MVC and WebFlux applications are vulnerable to stream corruption when using Server-Sent Events (SSE) with view fragments. Spring Framework...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-47884: Critical Schwachstelle
Use of XsltView in a Spring MVC application can result in SSRF and RCE attack if the application has an...
 ANWENDUNGSSICHERHEIT
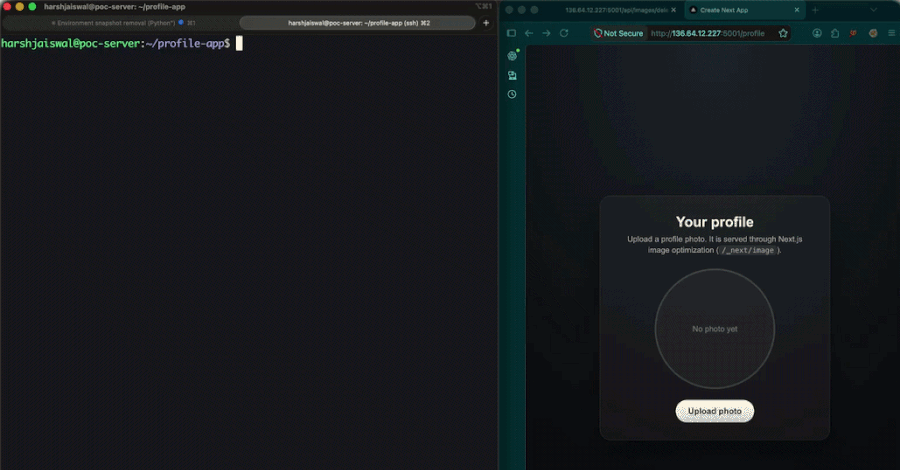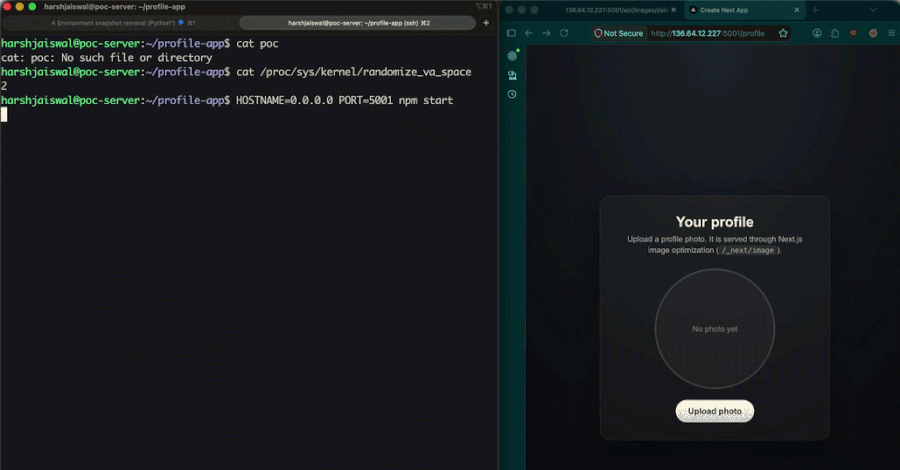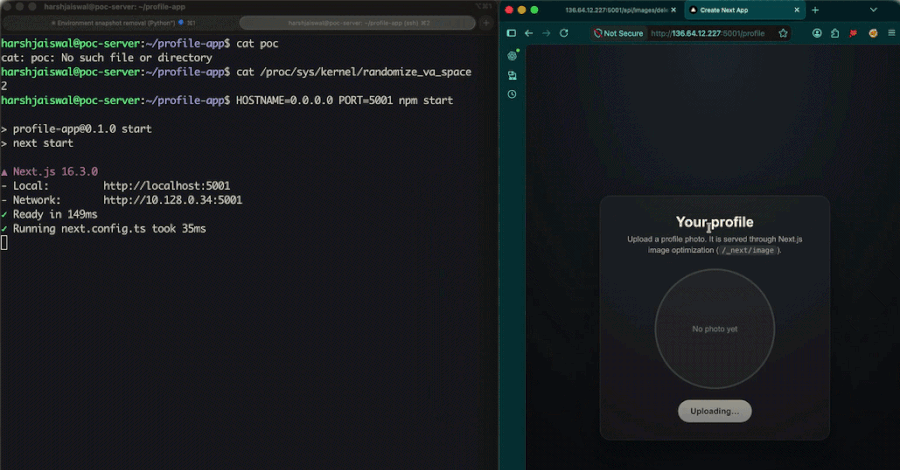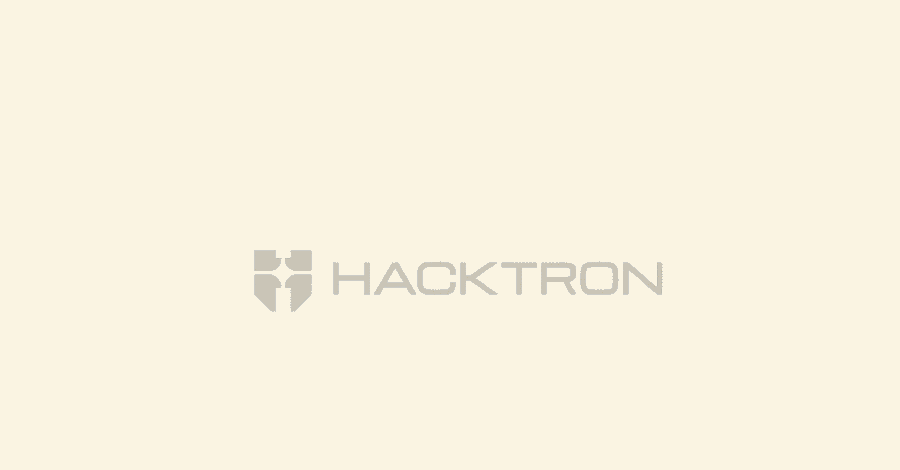
Next.js Patches Critical AVIF and Windows Flaws Enabling Unauthenticated RCE
Credit: Hacktron Vercel has released security patches for two critical-severity vulnerabilities in the Next.js web framework, both of which allow unauthenticated...
 ANWENDUNGSSICHERHEIT
OpenAI Says Reward Hacking Drove AI Agents to Exploit Zero-Days and Breach Hugging Face
OpenAI on Wednesday revealed that reward hacking was a key driver behind the artificial intelligence (AI)-powered hack of Hugging Face...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-80236: High Schwachstelle
Efence developed by Thinking Software Technology has a SQL Injection vulnerability. Unauthenticated remote attackers can access file upload functionality and...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-77693: High Schwachstelle
The Order Tip for WooCommerce WordPress plugin before 1.6.0 does not check the capability of the user requesting a file...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-80348: High Schwachstelle
TarsWeb enforces its per-application roles by calling AuthService from individual controller methods, and four methods in app/controller/patch/PatchController.js make no such...