Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
Citrix Patches 12 NetScaler and Secure Access Client Flaws, Including Authentication Bypass
Citrix has released patches for multiple critical security flaws impacting NetScaler ADC, Citrix NetScaler Gateway, and NetScaler Console that could...
 ANWENDUNGSSICHERHEIT
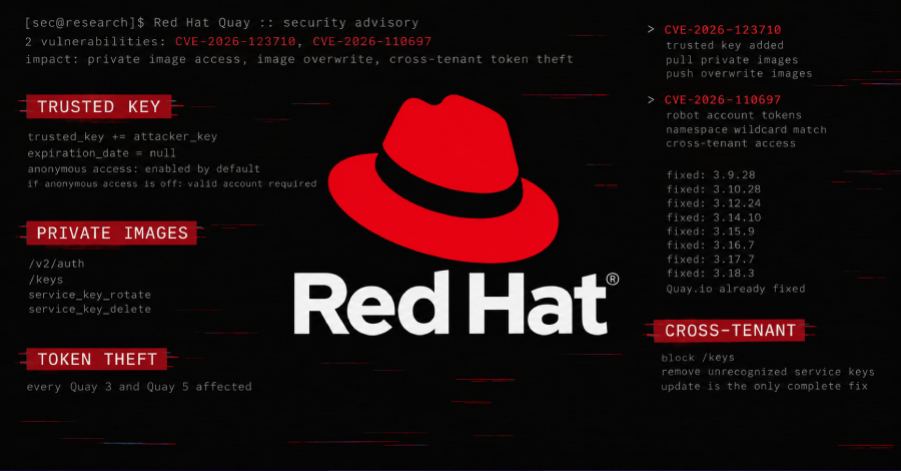
Critical Red Hat Quay Flaw Lets Attackers Read and Overwrite All Private Container Images in a Regis
A critical flaw in Red Hat Quay allows an attacker who can access a Quay registry to read and overwrite...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-118420: Medium Schwachstelle
The WP Directory Kit WordPress plugin before 1.6.3 does not sanitise and escape a parameter before using it in a...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-104718: Medium Schwachstelle
The Elementor Website Builder WordPress plugin before 4.3.6 does not validate or escape an element identifier before rendering it into...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-126611: High Schwachstelle
Progressive Robot hMailServer 6.3.4 through 6.3.7, with a MySQL or MariaDB database, TlsMode=verify-full and no TlsCaFile, does not verify the...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-12427: High Schwachstelle
The ARforms plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the 'description' parameter in all versions up to,...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-12424: High Schwachstelle
The ARforms plugin for WordPress is vulnerable to Stored Cross-Site Scripting via Referer Header in all versions up to, and...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-126610: High Schwachstelle
Progressive Robot hMailServer 6.3.4 through 6.3.7, with a MySQL or MariaDB database and TlsMode=verify-full, does not hand the database client...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-126623: High Schwachstelle
Inefficient algorithmic complexity in the JSON reader of Progressive Robot hMailServer 6.3.6 and 6.3.7 allows a remote attacker to hold...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-126621: High Schwachstelle
Progressive Robot hMailServer 6.0.0-B1 through 6.3.7 on Windows hands OpenSSL the names of its own TLS files - the listeners'...