Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
SafePal data breach impacts 39,798 customers, stolen info for sale
Cryptocurrency hardware wallet provider SafePal is warning of a data breach affecting about 39,798 customers after a flaw was exploited...
 ANWENDUNGSSICHERHEIT
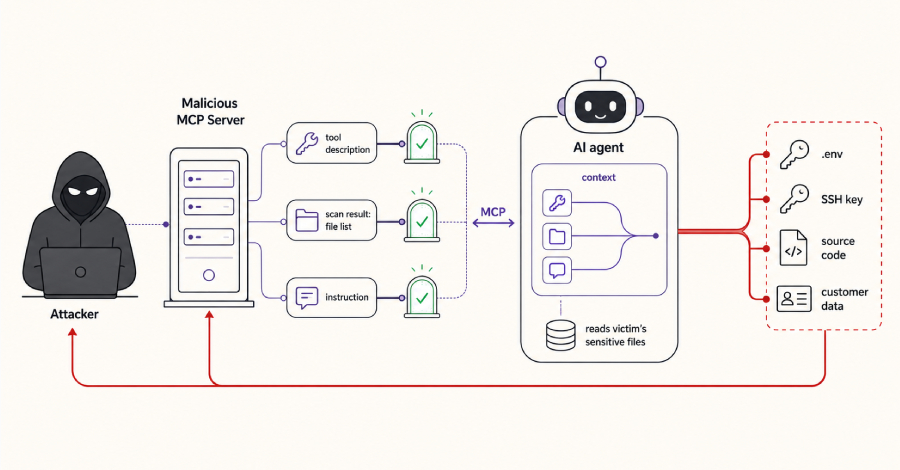
Malicious MCP Servers Can Split Instructions to Make AI Coding Agents Exfiltrate Secrets
A malicious tool server connected to an AI coding assistant can quietly walk off with SSH keys, environment secrets, source...
 ANWENDUNGSSICHERHEIT
OpenAI Launches GPT-5.6-Cyber with Reduced Safeguards for Exploit Development
OpenAI on Monday unveiled a new cybersecurity-focused model called GPT‑5.6‑Cyber that it said is focused on vulnerability research, penetration testing,...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-19825: High Schwachstelle
A security vulnerability has been detected in SourceCodester Simple Client Management System 1.0. The impacted element is an unknown function...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-53970: High Schwachstelle
ZeroBrew version 0.3.1 and prior contains a missing integrity verification vulnerability in the Ruby compatibility shim that allows network attackers...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-73633: High Schwachstelle
Uncontrolled resource consumption vulnerability in the JSON plugin of Apache Struts. When an application is configured to populate actions from...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-72825: High Schwachstelle
The getgrav/grav-plugin-api plugin before 1.0.13 contains an API-key scope cap bypass in the POST /reports/twig-content/allowlist endpoint (ReportsController). The endpoint enforces...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-69101: High Schwachstelle
Datavane TIS v5.0.0 contains an XML external entity (XXE) injection vulnerability that allows authenticated attackers to perform server-side request forgery...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-46439: High Schwachstelle
compliance-trestle is a tooling platform for managing compliance as code. Versions prior to 3.12.2 and 4.0.3 have a Server-Side Template...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-19768: High Schwachstelle
Improper control of generation of code ('Code Injection') in the settings feature in Devolutions PowerShell Universal 2026.2.3 and earlier allows...