Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-16538: Critical Schwachstelle
The Wallet for WooCommerce WordPress plugin before 1.6.10 does not verify the amount actually collected for a wallet top-up before...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-66659: Critical Schwachstelle
Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Essekia Tablesome Table allows Blind SQL...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2025-59326: Critical Schwachstelle
CPSD CryptoPro Secure Disk for Bitlocker before v7.7.4 fails to enforce IMA policy protections across temporary file systems, allowing for...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-26035: Critical Schwachstelle
An Improper Authentication vulnerability [CWE-287] vulnerability in Fortinet FortiWeb 8.0.0 through 8.0.2, FortiWeb 7.6.0 through 7.6.6, FortiWeb 7.4.0 through 7.4.11,...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-18391: Critical Schwachstelle
The WooCommerce Subscriptions WordPress plugin before 9.1.0 does not validate user input before unserializing it on stores with High-Performance Order...
 ANWENDUNGSSICHERHEIT
Lazarus Exploits Windows Zero-Day to Gain SYSTEM Access and Deploy Backdoor
The North Korean threat actor known as Lazarus Group has been attributed to the zero-day exploitation of a newly patched...
 ANWENDUNGSSICHERHEIT
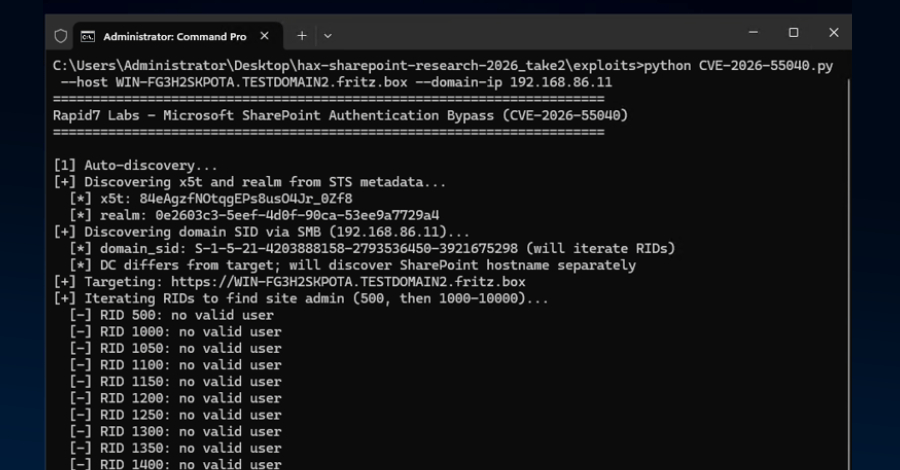
Attackers Exploit SharePoint Authentication Bypass After Public PoC Release
Threat actors have begun to exploit a newly disclosed Microsoft SharePoint vulnerability following the release of a proof-of-concept (PoC) code....
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-71217: High Schwachstelle
A flaw was found in iperf3. A remote attacker can exploit this vulnerability by sending crafted control-channel JSON with oversized...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-15565: High Schwachstelle
A flaw was found in Undertow. A remote attacker can cause Out of Memory on websockets endpoint without authentication on...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-50058: High Schwachstelle
A vulnerability has been identified in Solid Edge SE2025 (All versions < V225.0 Update 15), Solid Edge SE2026 (All versions...