Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-72599: Critical Schwachstelle
An SQL injection vulnerability in e107 2.4.0 allows unauthenticated remote attackers to execute arbitrary SQL via the news item page...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-72550: Critical Schwachstelle
An SQL injection vulnerability in Friendica through the 2026.08-dev branch allows unauthenticated remote attackers to execute arbitrary SQL statements via...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-72603: Critical Schwachstelle
An OS command injection vulnerability in wg-easy 15.3.0 allows users with the clients.create permission to execute arbitrary commands as root...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-58231: Critical Schwachstelle
SAP Commerce Cloud allows an unauthenticated attacker to abuse a default authentication client and submit specially crafted input to certain...
 ANWENDUNGSSICHERHEIT
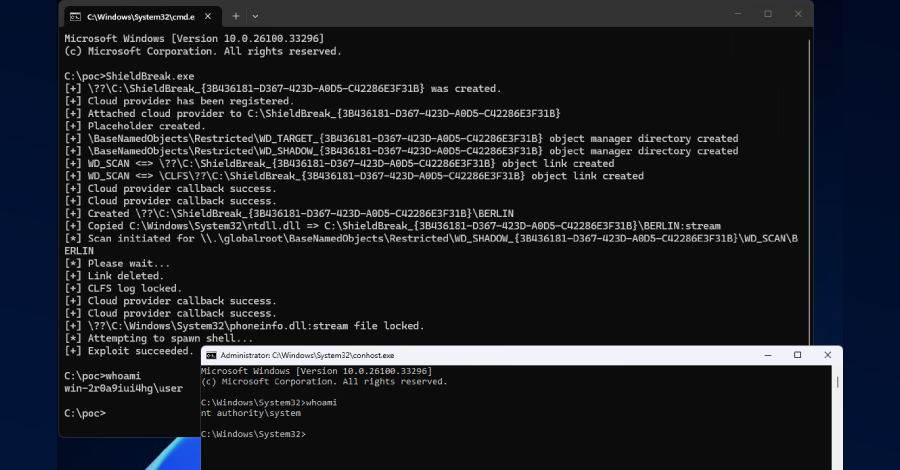
ShieldBreak Zero-Day PoC Claims Microsoft Defender Patch Bypass With SYSTEM Access
The security researcher going by the name Chaotic Eclipse (aka INFINITE NIGHTMARE, MSNightmare, and Nightmare-Eclipse) has released a proof-of-concept (PoC)...
 ANWENDUNGSSICHERHEIT
SAP Commerce Cloud Flaw Could Let Unauthenticated Attackers Execute Arbitrary Code
SAP has released patches to address a maximum-severity security flaw impacting Commerce Cloud (Data Hub Adapter) that could result in...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-17012: Medium Schwachstelle
The Accept PayPal & Stripe with Subscriptions for WooCommerce WordPress plugin through 3.1.0 does not verify that the PayPal account...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-18960: Medium Schwachstelle
The Block User Account WordPress plugin before 2.0.1 does not enforce its account block on every authentication path, allowing a...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-14941: Medium Schwachstelle
The Customer Reviews for WooCommerce WordPress plugin before 5.116.0 does not perform nonce or capability checks on several settings-related AJAX...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-16949: Medium Schwachstelle
The Term Pages WordPress plugin before 2.0.0 does not properly sanitise and escape a parameter before using it in a...