Cloud-Sicherheit
 CLOUD-SICHERHEIT
Infosecurity Europe: Patch Responsibility Remains Up for Grabs as AI Unearths Decades of Flaws
The emergence of AI models capable to autonomously find and fix vulnerabilities at scale is having a significant impact on...
 CLOUD-SICHERHEIT
Kirki, Burst Statistics WordPress Plugin Flaws in Attackers’ Crosshairs
Threat actors are exploiting vulnerable Kirki and Burst Statistics deployments to elevate privileges and take over websites. The post Kirki,...
 CLOUD-SICHERHEIT
China Uses Dual-Method Cyberattack on Czech Orgs
China is stealing data from high-value targets via a sneaky, double-layer spear-phishing campaign that includes the Azureveil malware....
 CLOUD-SICHERHEIT
FBI-Flagged Phishing Kit Kali365 Expands Its Reach
Once targeting just Microsoft 365, the phishing-as-a-service platform now aims at AWS, Okta, and Russian platforms, while relying on device...
 CLOUD-SICHERHEIT
🟡 CVE-2026-10241: Medium Schwachstelle
A security flaw has been discovered in jeecgboot The server processes these URLs up to 3.9.1. This affects the function...
 CLOUD-SICHERHEIT
🟠 CVE-2026-49298: High Luecke in Apache Airflow
A bug in Apache Airflow's KubernetesExecutor caused JWT tokens used by worker pods to authenticate against the Execution API to...
 CLOUD-SICHERHEIT
🔴 CVE-2026-7858: Critical Schwachstelle
A Deserialization of Untrusted Data vulnerability affecting Teamwork Cloud from No Magic Release 2022x through No Magic Release 2026x and...
 CLOUD-SICHERHEIT
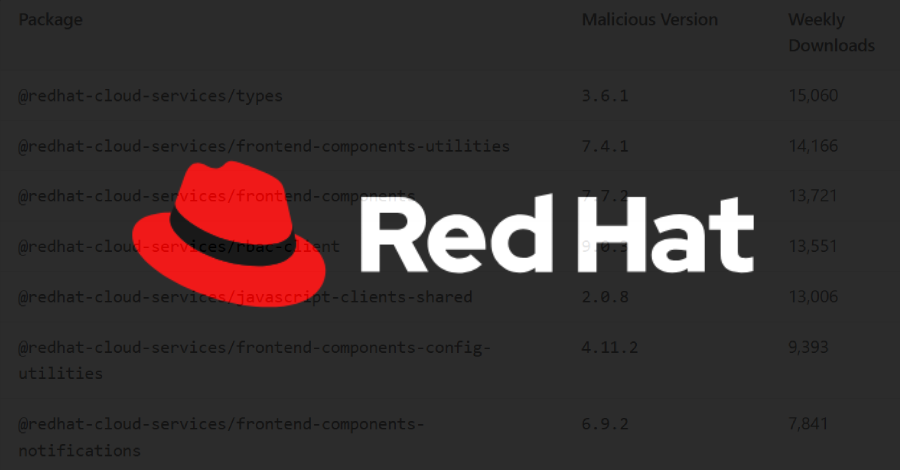
Red Hat npm packages compromised to steal developer credentials
More than 30 npm packages under Red Hat's '@redhat-cloud-services' namespace were compromised in a supply-chain attack that distributed a new...
 CLOUD-SICHERHEIT
Miasma Supply Chain Attack Compromises Red Hat npm Packages with Credential-Stealing Worm
A new Mini Shai-Hulud supply chain attack campaign, codenamed Miasma, has compromised @redhat-cloud-services packages to steal credentials and secrets from...
CLOUD-SICHERHEIT
🟡 CVE-2026-10177: Medium Schwachstelle
A security vulnerability has been detected in Aider-AI Aider 0.86.3. This affects the function requests.get of the file api_docs.py of...