Cloud-Sicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-15416: High Schwachstelle
A flaw was identified in Argo CD, the GitOps engine used by Red Hat OpenShift GitOps, that could allow an...
 CLOUD-SICHERHEIT
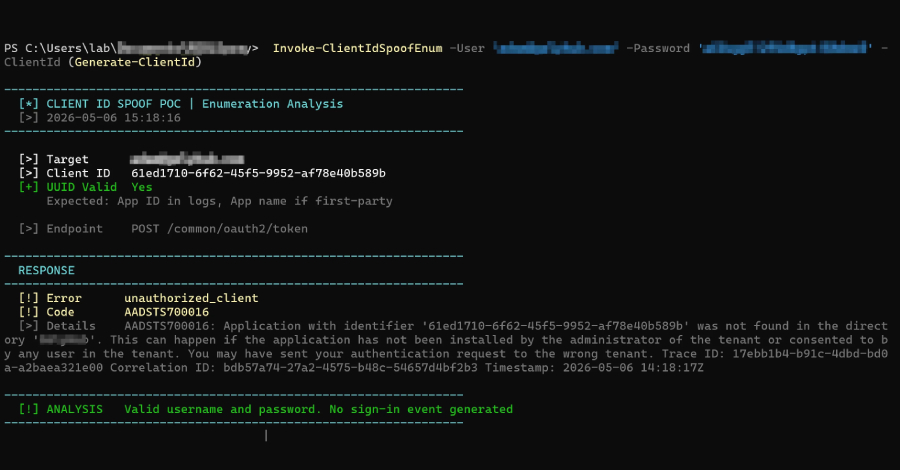
OAuth Client ID Spoofing Lets Attackers Validate Stolen Microsoft Entra Credentials
At least two distinct threat actors are weaponizing a novel evasion technique called OAuth client ID spoofing in cloud campaigns,...
 CLOUD-SICHERHEIT
RabbitMQ Flaws Could Leak OAuth Secrets and Expose Cross-Tenant Queue Metadata
Cybersecurity researchers have disclosed details of two access control-related flaws impacting the RabbitMQ message broker service that could allow attackers...
 CLOUD-SICHERHEIT
🟡 CVE-2026-49876: Medium Luecke in Apache Gravitino
Authenticated SSRF in Gravitino JobManager allows server-side HTTP requests to internal network and cloud metadata endpoints via unvalidated job template...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-57363: High Schwachstelle
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in QuantumCloud ChatBot chatbot allows Stored XSS.This issue affects...
 CLOUD-SICHERHEIT
Organizations Warned of Exploited Joomla Extension Vulnerabilities
Threat actors have been targeting Balbooa Forms and iCagenda Joomla extension flaws for remote code execution. The post Organizations Warned...
 CLOUD-SICHERHEIT
Lessons Learned from CISA’s Recent GitHub Leak
The Cybersecurity and Infrastructure Security Agency (CISA) has issued a postmortem on a data leak in which a contractor published...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-15512: Medium Schwachstelle
A vulnerability was identified in pig-mesh Pig up to 3.9.2. Affected by this issue is some unknown functionality of the...
CLOUD-SICHERHEIT
🟡 CVE-2026-15508: Medium Schwachstelle
A flaw has been found in Helicone ai-gateway up to 0.2.0-beta.30. This affects the function build_target_url of the file ai-gateway/src/dispatcher/service.rs...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-15496: Medium Schwachstelle
A vulnerability was found in SonicCloudOrg sonic-agent up to 2.7.2. The impacted element is the function evalIsFailed of the file...