Endpunktsicherheit
 ENDPUNKTSICHERHEIT
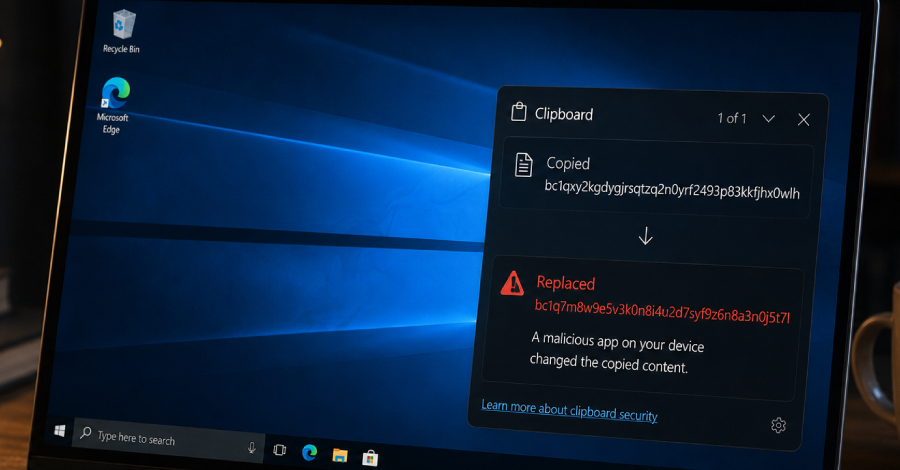
Microsoft Details Windows Clipper Malware Campaign Using USB LNK Worm and Tor-Based C2
Microsoft has disclosed details of a Windows-based cryptocurrency clipper campaign that has targeted users since February 2026 with clipboard-intercepting malware...
 ENDPUNKTSICHERHEIT
China-Linked SprySOCKS Backdoor Expands to Windows with Driver-Based Stealth
Cybersecurity researchers have flagged two previously undocumented Windows variants of what was believed to be a Linux-only backdoor called SprySOCKS....
 ENDPUNKTSICHERHEIT
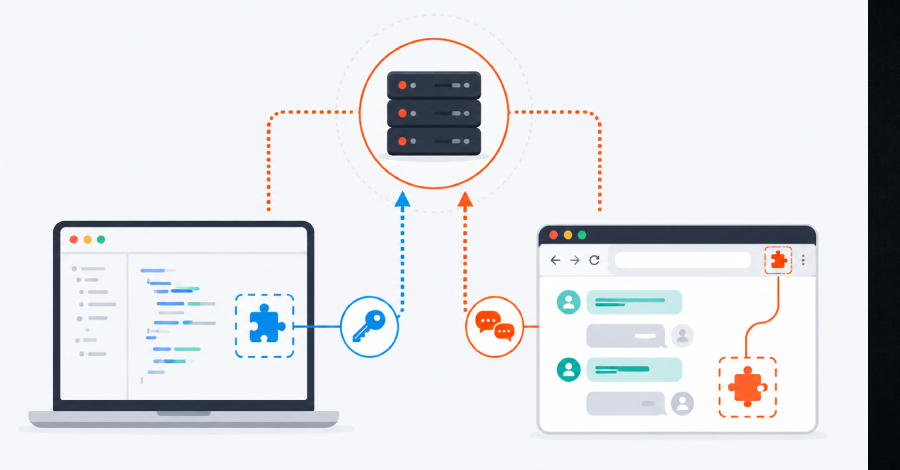
Malicious JetBrains Plugins Steal AI API Keys as Chrome Extensions Capture Chatbot Chats
Cybersecurity researchers have flagged a "coordinated malware campaign" on the JetBrains Marketplace that has published no less than 15 malicious...
 ENDPUNKTSICHERHEIT
🟡 CVE-2026-50255: Medium Schwachstelle
Incorrect default permissions issue exists in Optical Disc Archive Software for Windows 5.5.3 and earlier. If this vulnerability is exploited,...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-12398: High Schwachstelle
A command injection vulnerability was found in galaxy_ng. The do_git_checkout() function in the legacy role import API (v1) interpolates unsanitized...
 ENDPUNKTSICHERHEIT
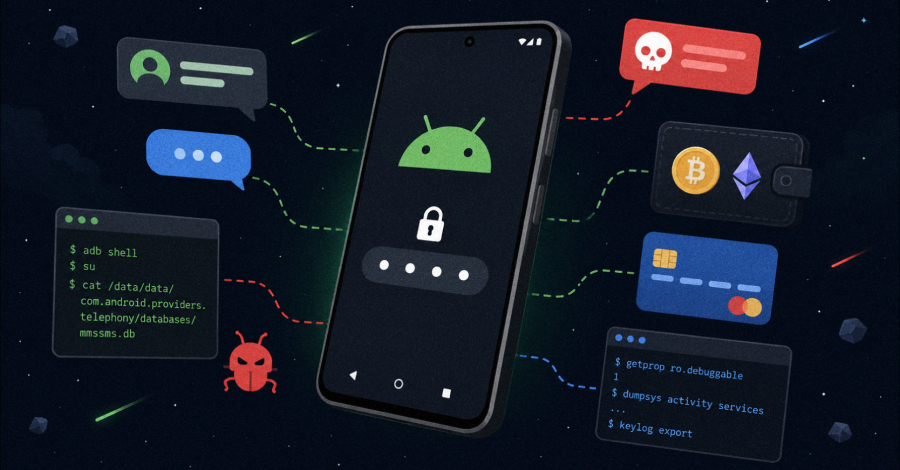
New Rokarolla Android Malware Steals PINs, SMS Codes, and Crypto Wallet Funds
Security researchers at Zimperium's zLabs have documented a new Android banking trojan, Rokarolla, that targets 217 banking and cryptocurrency apps and packs...
 ENDPUNKTSICHERHEIT
ClickFix Campaigns Expand Malware Delivery With New Loaders and Fake Update Lures
Cybersecurity researchers have flagged multiple ClickFix campaigns that deliver three malware loaders called BabaDeda Loader, Lorem Ipsum Loader, and Potemkin,...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2016-20083: Medium Schwachstelle
WordPress More Fields Plugin 2.1 contains a cross-site request forgery vulnerability that allows attackers to perform unauthorized actions by disabling...
 ENDPUNKTSICHERHEIT
🟡 CVE-2026-8386: Medium Schwachstelle
The WP Go Maps WordPress plugin before 10.0.10 does not perform any approval-state filtering on its public single-marker REST endpoint,...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-11931: Medium Schwachstelle
Incorrect default permissions in Kiro IDE on macOS and Linux before version 0.11.133 could expose the authentication token cache file...