Endpunktsicherheit
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-112082: High Schwachstelle
A vulnerability was identified in sgl-project SGLang up to 0.5.19. This impacts the function Scheduler.expert_distribution_handle of the file python/sglang/srt/eplb/expert_distribution.py of...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-80312: High Schwachstelle
Improper Authentication vulnerability in Apache Camel OAuth component. This issue affects Apache Camel: from 4.11.0 before 4.18.5, from 4.19.0 before...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-78164: High Schwachstelle
Improper Neutralization of Special Elements Used in a Template Engine and Exposure of Sensitive Information to an Unauthorized Actor vulnerability...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-78165: High Schwachstelle
Deserialization of Untrusted Data vulnerability in Apache Camel Spring Redis component. This issue affects Apache Camel: from 2.11.0 before 4.18.5,...
 ENDPUNKTSICHERHEIT
Popular WordPress SEO Plugin Rank Math PRO Hijacked to Deliver Self-Restoring Backdoor
Copies of Rank Math PRO, the paid version of the Rank Math SEO plugin for WordPress, that were downloaded from...
 ENDPUNKTSICHERHEIT
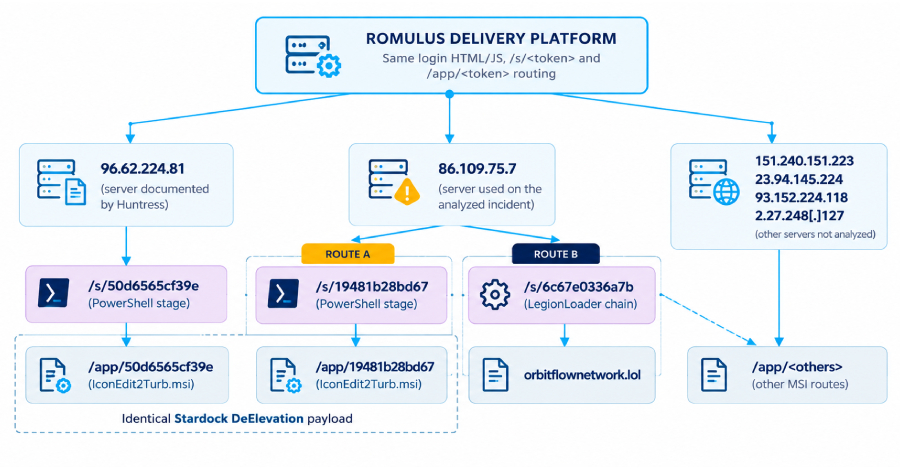
Hackers Use New ROMULUS ClickFix Platform to Deliver LegionLoader and Other Malware
Cybersecurity researchers have disclosed details of a ClickFix delivery platform called ROMULUS that's being used to distribute malware such as...
 ENDPUNKTSICHERHEIT
🟡 CVE-2026-112051: Medium Schwachstelle
Xinference through 4.0.1 contains a path traversal vulnerability on Windows that allows unauthenticated attackers to write and delete arbitrary .json...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-112017: Medium Schwachstelle
JeecgBoot before 3.9.5 contains an sql injection vulnerability that allows authenticated attackers to bypass the SqlInjectionUtil keyword blocklist by inserting...
 ENDPUNKTSICHERHEIT
Attackers Tampered with AOMEI Backupper’s Update Servers for Minutes to Deliver a Backdoor
Attackers repeatedly changed the files that AOMEI Backupper fetches from the vendor's own update servers, in windows of five to...
 ENDPUNKTSICHERHEIT
MALFEX npm Package ‚imgdecode‘ Hides Shellcode Loader in Windows Native Addon
Cybersecurity researchers have discovered a malicious npm package that's part of a recently disclosed software supply chain attack campaign dubbed...