Endpunktsicherheit
 ENDPUNKTSICHERHEIT
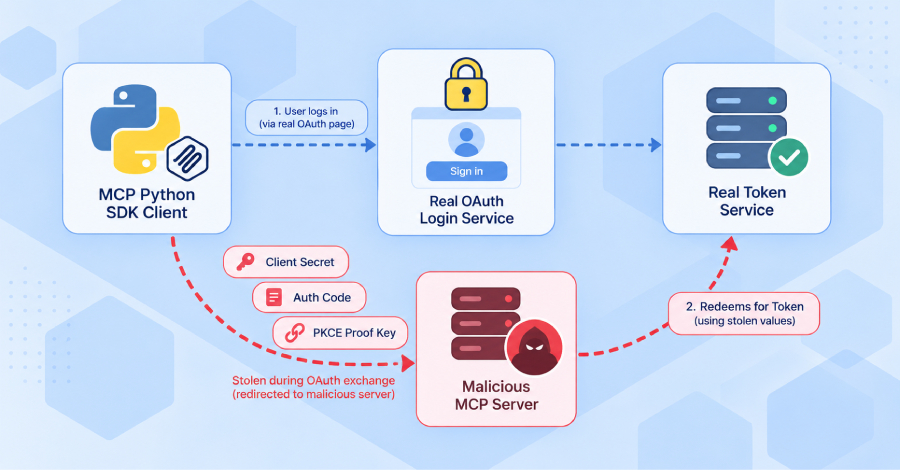
Official MCP Python SDK Flaw Can Let Malicious Servers Steal OAuth Credentials
A malicious MCP server could trick an application built on the official MCP Python SDK into handing over the OAuth credentials it...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-101050: Medium Schwachstelle
Heym before 0.0.53 fails to verify the X-Telegram-Bot-Api-Secret-Token header on Telegram webhook endpoints when credential_id is absent or secret_token is...
 ENDPUNKTSICHERHEIT
🟡 CVE-2026-96899: Medium Schwachstelle
The Optima Express IDX WordPress plugin before 8.7.6 does not properly neutralise a script value submitted through one of its...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-101059: High Schwachstelle
utcp-http before 1.1.4 fails to validate the OAuth2 tokenUrl field from remote OpenAPI specifications, allowing attackers to redirect credential submission...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-96896: High Schwachstelle
The Malcure Malware Shield — Removal, Repair, Monitor WordPress plugin before 19.9.7 does not perform an authorisation check on one...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-100885: High Schwachstelle
A vulnerability was found in Krayin laravel-crm up to 2.2.4. This affects an unknown function of the file packages/Webkul/Installer/src/Http/Middleware/CanInstall.php of...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-101064: High Schwachstelle
Obot before v0.23.0 contains a server-side request forgery vulnerability in remote MCP server registration that allows privileged users to specify...
 CLOUD-SICHERHEIT
🟠 CVE-2026-101060: High Schwachstelle
python-utcp versions before 1.1.4 contain a server-side request forgery vulnerability in HttpCommunicationProtocol.call_tool that validates the initial tool URL but follows...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-101062: High Schwachstelle
Obot before v0.23.0 (affected versions
ENDPUNKTSICHERHEIT
🟠 CVE-2026-100871: High Schwachstelle
Sylius versions before 1.12.25, 1.13.17, 1.14.20, 2.1.16, and 2.2.9 fail to include firewall identification in JWT tokens issued by separate...