Endpunktsicherheit
 ENDPUNKTSICHERHEIT
How Threat Actors Are Turning Trusted AI Platforms Into an Attack Surface
Threat actors are abusing trusted AI platforms to host malicious content, poison search results, and trick users into installing malware....
 ENDPUNKTSICHERHEIT
Hackers abused Claude to extract secrets from 1.8M Android apps
Anthropic says multiple threat groups, including the financially motivated and state-sponsored espionage groups linked to Russia and China, tried to...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-89250: High Schwachstelle
WWBN AVideo through commit c3edcc274c389816d434acadac07ee78eaf330c1 contains an unauthenticated file read vulnerability in the getRecordedFile.php endpoint that streams recorded FLV files...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-38058: High Schwachstelle
The endpoint on the iDirect iQ200 VSAT terminal returns the complete device configuration as JSON, including the SECURITY section which...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-89254: High Schwachstelle
AVideo through commit c3edcc274c389816d434acadac07ee78eaf330c1 contains a stored cross-site scripting vulnerability in the CustomizeUser plugin where the field_name parameter is stored...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-89176: High Schwachstelle
WeenyGenius, a computer lab management system developed by Howyar Technologies, has a Missing Authentication vulnerability. Unauthenticated attackers on the same...
 ENDPUNKTSICHERHEIT
Gigabud Creates Android Work Profiles to Hide From Banking App Malware Checks
The Gigabud banking trojan now installs a second Android app that creates a work profile on an infected phone and...
 ENDPUNKTSICHERHEIT
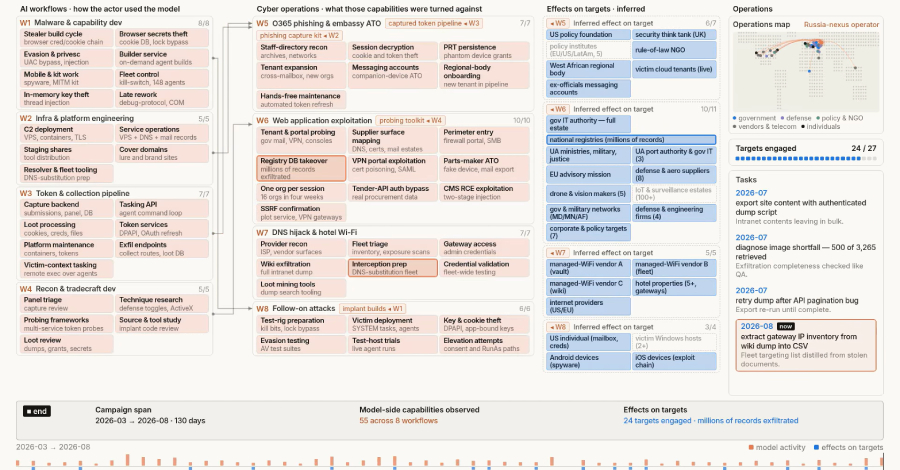
Russian State-Sponsored Hackers Use Claude to Rebuild Malware After Detection
Anthropic on Thursday revealed it disrupted a campaign mounted by a Russian state-sponsored threat actor that abused Claude for developing...
ENDPUNKTSICHERHEIT
🟠 CVE-2026-77771: High Schwachstelle
The miniOrange 2FA WordPress plugin before 6.3.1, miniOrange 2FA WordPress plugin before 19.3 does not scope its second-factor attempt limit...
ENDPUNKTSICHERHEIT
🟠 CVE-2026-64836: High Schwachstelle
ICEcoder versions through 8.1 contain a path traversal vulnerability in the file-control endpoint due to a logic error in the...