Endpunktsicherheit
 CLOUD-SICHERHEIT
🟠 CVE-2026-123059: High Schwachstelle
In Eclipse BaSyx Helm Charts version 2.2.0 of the `aas-basyx-v2-full` chart, deployments with the bundled Keycloak enabled store the client...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-107912: High Schwachstelle
A flaw was found in the management interface of the Quarkus framework, specifically within the quarkus-vertx-http component. The issue occurs...
 ENDPUNKTSICHERHEIT
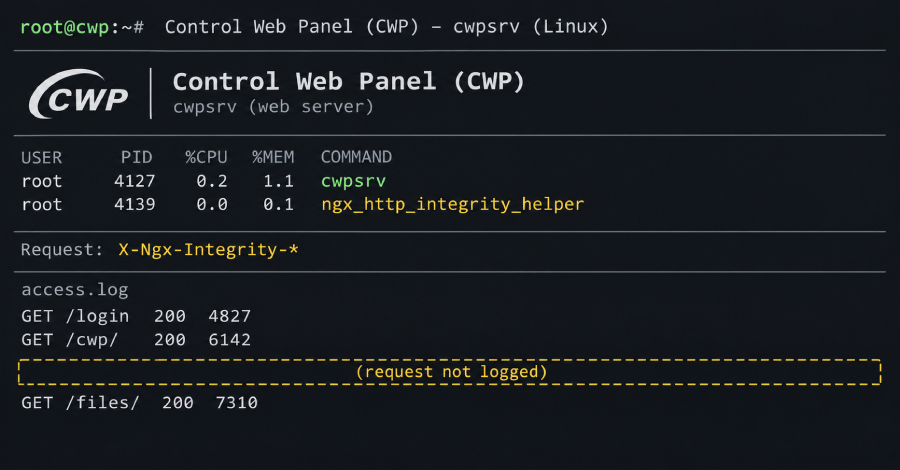
Hackers backdoor Linux servers using trojanized CWP web server
A new Linux malware called CWPdoor is being distributed through a trojanized version of cwpsrv, the web server behind the...
 ENDPUNKTSICHERHEIT
Hackers Hide Linux Backdoor in Control Web Panel Server to Execute Commands Without Logs
A backdoor has been found hiding in the web server that runs Control Web Panel (CWP), a free panel for...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-118422: High Schwachstelle
The Stape Conversion Tracking WordPress plugin before 2.3.11 does not validate the sub-path appended to its same-origin proxy's upstream endpoint,...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-59264: High Luecke in Apache Openoffice
The Windows installers of Apache OpenOffice 4.1.16 and earlier allow an already manipulated system to run external code with elevated...
 ENDPUNKTSICHERHEIT
Why Urgent Security Fixes Aren’t Fixed. Observe, Prove, Act, Confirm Gets Them Moving
The alert is critical. The fix is known. And the ticket sits in a queue for days. Security teams understand...
 ENDPUNKTSICHERHEIT
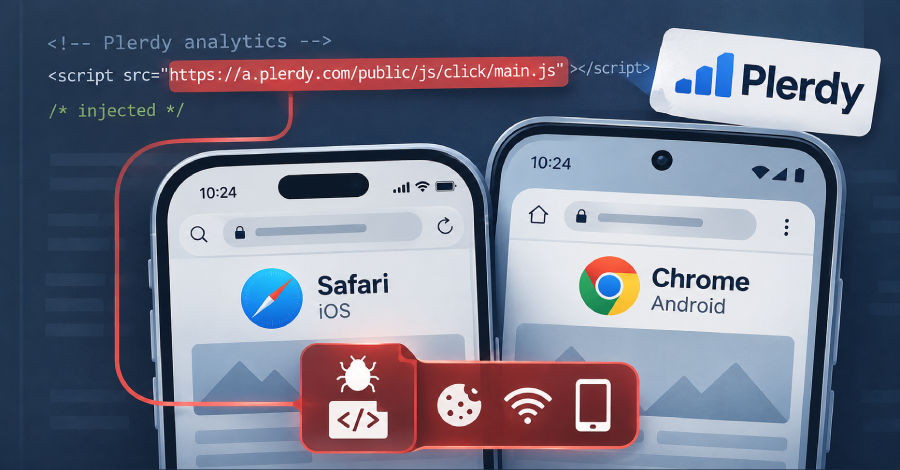
APT29-Linked Hackers Hijack Web Analytics Script to Deliver iOS and Android Exploits
The Russia-linked threat actor known as APT29 is presumed to be behind a large-scale watering hole campaign targeting iOS and...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-103379: Medium Schwachstelle
The WATI Chat and Notification WordPress plugin through 1.1.8 does not require a valid, non-empty secret on a public endpoint...
ENDPUNKTSICHERHEIT
🟡 CVE-2026-121024: Medium Schwachstelle
Incorrect Authorization (CWE-863) in the Health Monitoring service in AxxonSoft AxxonNet before 3.28.0 on Linux allows a remote attacker in...