Endpunktsicherheit
 ENDPUNKTSICHERHEIT
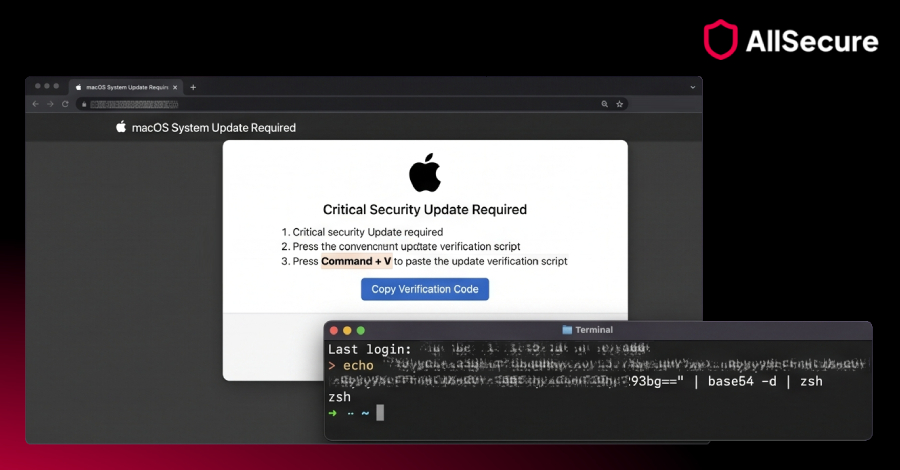
DPRK-Linked macOS Malvertising Uses Fake Updates to Deliver Crypto-Stealing Malware
Threat actors with ties to North Korea have been attributed to a sophisticated macOS malvertising campaign that involves redirecting users...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-18220: High Schwachstelle
An out-of-bounds write vulnerability was found in the BFD library's DLX ELF backend (bfd/elf32-dlx.c) in GNU binutils. The dlx_rtype_to_howto() function...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-64556: High Schwachstelle
In the Linux kernel, the following vulnerability has been resolved: perf/core: Detach event groups during remove_on_exec perf_event_remove_on_exec() removes events by...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-63231: High Schwachstelle
A post-authentication SQL injection vulnerability in Koollab LMS allowed an authenticated attacker to use an error-based SQL oracle via the...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-50622: High Schwachstelle
Description: Missing Authorization in Apache Atlas. A missing authorization vulnerability in Apache Atlas's admin endpoints allows any authenticated user, regardless of...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-64557: High Schwachstelle
In the Linux kernel, the following vulnerability has been resolved: Bluetooth: L2CAP: Fix use-after-free in l2cap_sock_new_connection_cb() l2cap_sock_new_connection_cb() returned l2cap_pi(sk)->chan ...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-63230: Critical Schwachstelle
A pre-authentication error-based SQL injection vulnerability in Koollab LMS allowed an unauthenticated attacker to read sensitive database contents, including personally...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-63229: Critical Schwachstelle
A pre-authentication blind SQL injection vulnerability in Koollab LMS allowed an unauthenticated attacker to use a time-based SQL oracle via...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-63234: Critical Schwachstelle
A SQL injection and unsafe deserialisation vulnerability in Koollab LMS allowed an authenticated attacker to inject through the manual mark...
ANWENDUNGSSICHERHEIT
🔴 CVE-2026-63233: Critical Schwachstelle
A SQL injection and unsafe deserialisation vulnerability in Koollab LMS allowed an authenticated attacker to inject through the assessment overall...