Endpunktsicherheit
 ENDPUNKTSICHERHEIT
🔴 CVE-2026-16242: Critical Schwachstelle
A flaw was found in the Konnectivity proxy-server configuration for hosted control planes. The agent-facing listener was started without --cluster-ca-cert...
 ENDPUNKTSICHERHEIT
FakeGit Campaign Uses 7,600 GitHub Repositories to Spread SmartLoader Malware
Cybersecurity researchers have discovered nearly 7,600 malicious GitHub repositories, out of which more than 800 pose as artificial intelligence (AI)...
 ENDPUNKTSICHERHEIT
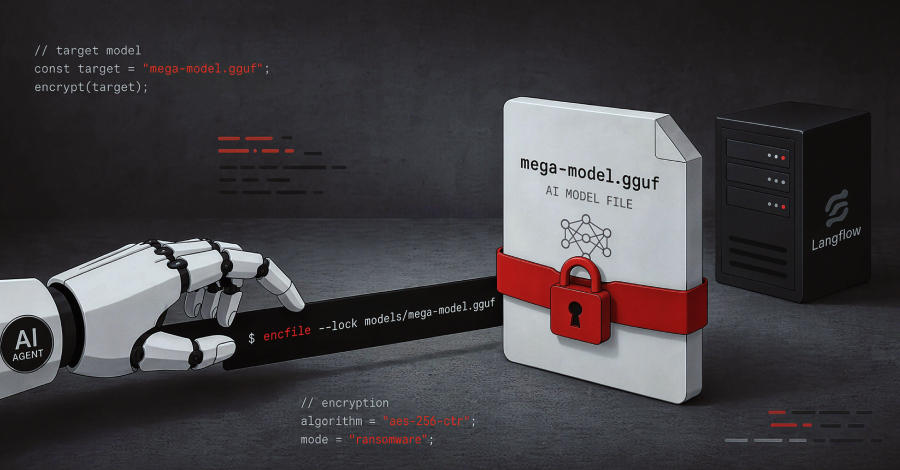
New ENCFORGE Ransomware Targets AI Model Files in Langflow RCE Attack
Researchers at Sysdig have linked a second attack on the same Langflow server to JADEPUFFER, the AI-agent-driven operator it first...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-63816: High Schwachstelle
In the Linux kernel, the following vulnerability has been resolved: f2fs: atomic: fix UAF issue on f2fs_inode_info.atomic_inode - ioctl(F2FS_IOC_GARBAGE_COLLECT_RANGE) -...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-63814: High Schwachstelle
In the Linux kernel, the following vulnerability has been resolved: f2fs: validate ACL entry sizes in f2fs_acl_from_disk() f2fs_acl_count() only validates...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-63813: High Schwachstelle
In the Linux kernel, the following vulnerability has been resolved: Revert "f2fs: remove non-uptodate folio from the page cache in...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-63812: High Schwachstelle
In the Linux kernel, the following vulnerability has been resolved: f2fs: fix incorrect FI_NO_EXTENT handling in __destroy_extent_node() When __destroy_extent_node() sets...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-63809: High Schwachstelle
In the Linux kernel, the following vulnerability has been resolved: bpf: use kvfree() for replaced sysctl write buffer proc_sys_call_handler() allocates...
ENDPUNKTSICHERHEIT
🟠 CVE-2026-63805: High Schwachstelle
In the Linux kernel, the following vulnerability has been resolved: crypto: nx - fix nx_crypto_ctx_exit argument nx_crypto_ctx_shash_exit calls nx_crypto_ctx_exit with...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-63803: High Schwachstelle
In the Linux kernel, the following vulnerability has been resolved: hdlc_ppp: sync per-proto timers before freeing hdlc state Each PPP...