Netzwerksicherheit
 NETZWERKSICHERHEIT
Iran-Linked Handala Hack Tied to HEAVYGRAM Telegram Backdoor That Can Steal Passwords
The Iran-linked "hacktivist" persona known as Handala Hack has been attributed to a Telegram-based surveillance backdoor called HEAVYGRAM and a...
 NETZWERKSICHERHEIT
Critical Check Point Management Flaw Lets Unauthenticated Attackers Run Code as Root
A critical vulnerability in Check Point's Security Management and Log Servers could allow an attacker without login credentials to run...
 CLOUD-SICHERHEIT
🟠 CVE-2026-2380: High Schwachstelle
On affected platforms running Arista EOS with OpenConfig-related services (i.e., gNMI, gNSI, RESTCONF and NETCONF), sensitive requests and responses may...
 NETZWERKSICHERHEIT
🟠 CVE-2026-81634: High Schwachstelle
In NLnet Labs Unbound up to and including 1.26.0, a 255 length query name with a large TCP response can...
 NETZWERKSICHERHEIT
🟠 CVE-2026-88263: High Schwachstelle
XikeStor Layer3 switches miss authentication for downloading configuration data. Unauthenticated attacker may retrieve the configuration data containing network configurations and...
 NETZWERKSICHERHEIT
🟠 CVE-2026-73454: High Schwachstelle
On affected platforms running Arista EOS with gRPC Network Security Interface (gNSI) Credentialz configured, a specially crafted request can cause...
 NETZWERKSICHERHEIT
🟠 CVE-2026-73464: High Schwachstelle
On affected platforms running Arista EOS with gRPC Network Management Interface (gNMI) enabled, a specially crafted request could allow a...
 NETZWERKSICHERHEIT
🔴 CVE-2026-73447: Critical Schwachstelle
A privileged attacker can exploit certain operation to execute arbitrary commands with root privileges, leading to full device compromise. An...
 NETZWERKSICHERHEIT
‚Sandworm‘ Chains Cisco Vulnerabilities to Deploy Cyclops Blink
The notorious Russian threat group is spreading an upgraded version of the botnet malware, which the FBI disrupted in 2022....
 NETZWERKSICHERHEIT
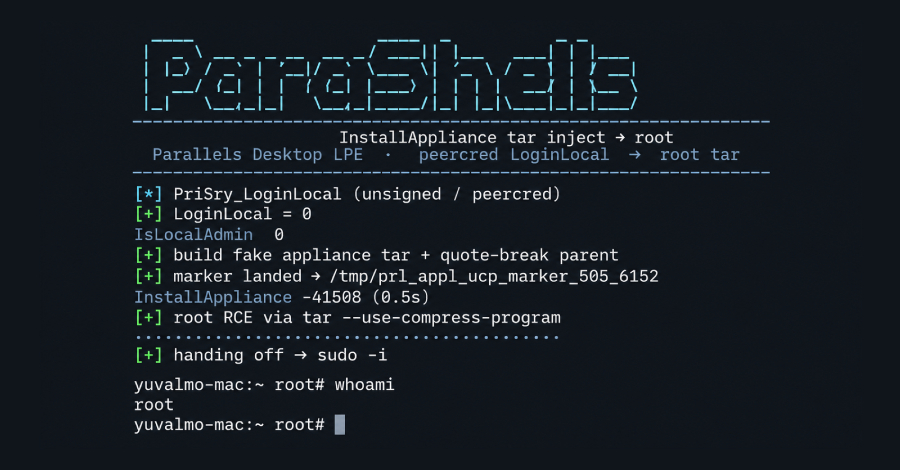
Parallels Desktop Flaw Lets Non-Admin Mac Users Gain Root, but Intel Macs Can’t Install Fix
Parallels Desktop for Mac has a flaw that lets an ordinary local account run code as root, the highest level...