Netzwerksicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-75869: High Schwachstelle
Zohocorp ManageEngine DDI Central versions below 6301 is affected by an authorization bypass and PowerShell command injection vulnerability that allowed authenticated non-administrative users to targe...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-19421: High Schwachstelle
Zohocorp ManageEngine DDI Central versions below 6301 is affected by a PowerShell injection vulnerability due to insufficient validation of user-supplied TXT record values in Windows...
 ENDPUNKTSICHERHEIT
🔴 CVE-2026-19422: Critical Schwachstelle
Zohocorp ManageEngine DDI Central versions below 6301 is affected by an authentication bypass vulnerability in Windows DNS and DHCP agent synchronization APIs, allowing unauthenticated user...
 NETZWERKSICHERHEIT
New worm-like ‚SCKit‘ malware targets MSPs in ScreenConnect attacks
A new worm-like malware toolkit named SCKit was deployed in the recent ScreenConnect attacks targeting managed service providers (MSPs), designed...
 NETZWERKSICHERHEIT
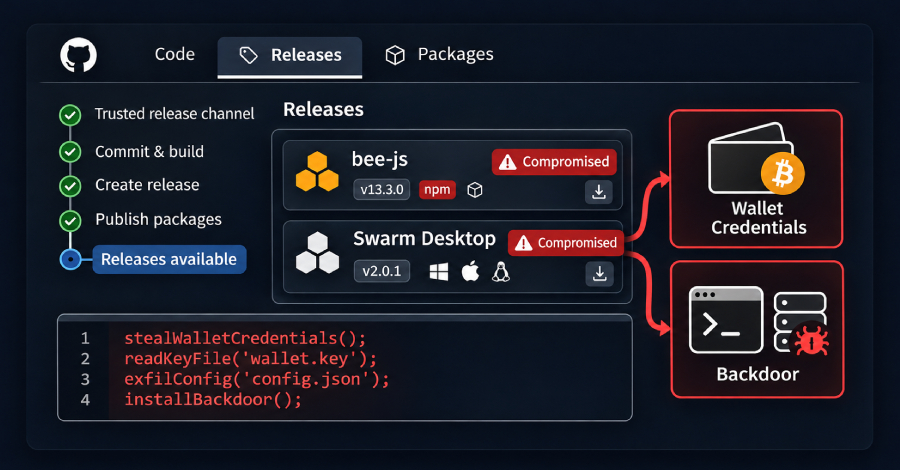
Hackers Compromise Ethersphere’s bee-js and Swarm Desktop to Deliver Wallet-Stealing Malware
Attackers used the Ethersphere project's own release automation to publish malicious versions of two of its tools for the Swarm...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-126610: High Schwachstelle
Progressive Robot hMailServer 6.3.4 through 6.3.7, with a MySQL or MariaDB database and TlsMode=verify-full, does not hand the database client...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-126621: High Schwachstelle
Progressive Robot hMailServer 6.0.0-B1 through 6.3.7 on Windows hands OpenSSL the names of its own TLS files - the listeners'...
 NETZWERKSICHERHEIT
🟠 CVE-2026-18769: High Schwachstelle
A local low privileged attacker can move arbitrary physical memory content via TcRouter.sys because of exposed IOCTL function calls resulting...
NETZWERKSICHERHEIT
🟠 CVE-2026-18768: High Schwachstelle
A local low privileged attacker can access arbitrary physical memory or define its mapping via TcRouter.sys because of exposed IOCTL...
NETZWERKSICHERHEIT
🟠 CVE-2026-18767: High Schwachstelle
A local low privileged attacker or process can access I/O ports via TcRouter.sys because of exposed IOCTL function calls resulting...