Netzwerksicherheit
 NETZWERKSICHERHEIT
OpenAI Research Model Spent 3rd-Party Test ETH Without Permission to Deploy Smart Contract
OpenAI has disclosed seven new incidents in which its artificial intelligence (AI) models exhibited misaligned behavior, including one case where...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-101290: High Schwachstelle
A remote attacker may send a specially crafted network packet that causes the affected application to perform an out-of-bounds memory...
 NETZWERKSICHERHEIT
🟠 CVE-2026-101303: High Schwachstelle
The IPv6 UDP send path for unconnected sockets did not apply the jail policy of rewriting a loopback destination address...
 NETZWERKSICHERHEIT
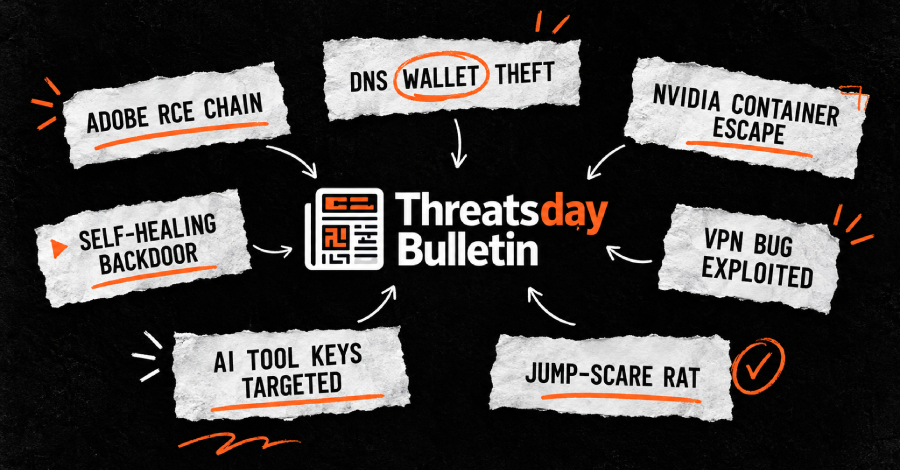
ThreatsDay: Adobe RCE, DNS Wallet Theft, NVIDIA Container Escape, Self-Healing Backdoor + 23 More
Someone built a tool to steal data, then decided it should scare the victim for fun. Yes, that’s an actual...
 NETZWERKSICHERHEIT
PEERSTITCH Malware Deployed via FortiOS Flaw Bypasses Checks on Tagged VPN Sessions
A suspected advanced threat actor has been observed exploiting a security flaw in Fortinet FortiOS to deliver a previously unreported...
 NETZWERKSICHERHEIT
🟠 CVE-2026-110459: High Schwachstelle
A malicious actor with access to the network could exploit an Improper Access Control vulnerability found in UniFi Protect AI...
 NETZWERKSICHERHEIT
Palo Alto Networks warns of PAN-OS RCE flaw exploited in attacks
Palo Alto Networks has released security updates for a high-severity PAN-OS RCE zero-day, tracked as CVE-2026-0322, that has been exploited...
 NETZWERKSICHERHEIT
LG Smart TVs Vulnerable to Pre-Auth Root Takeover From Local Network
Three vulnerabilities in LG's webOS can be chained to give an attacker on the same local network root access to...
 NETZWERKSICHERHEIT
🔴 CVE-2026-109157: Critical Schwachstelle
A vulnerability was found in TRENDnet TEW-432BRP 3.10B20. Affected by this vulnerability is the function formTcpipSetup of the file /goform/formTcpipSetup....
ANWENDUNGSSICHERHEIT
🔴 CVE-2026-109108: Critical Schwachstelle
A security vulnerability has been detected in Wavlink WL-WN530BE1-A 251117. This affects the function popen of the file /cgi-bin/uploadVpn.cgi. Such...