Netzwerksicherheit
 NETZWERKSICHERHEIT
SonicWall Patches CVSS 10.0 Pre-Authentication SSRF Flaw in SMA1000 Appliances
SonicWall has released hotfixes for four flaws in its SMA1000 appliances, the gateways that give remote workers access to a...
 NETZWERKSICHERHEIT
Engineer sentenced for locking over 3,000 devices on employer network
A former core infrastructure engineer at an industrial company headquartered in New Jersey was sentenced to 32 months in prison...
 NETZWERKSICHERHEIT
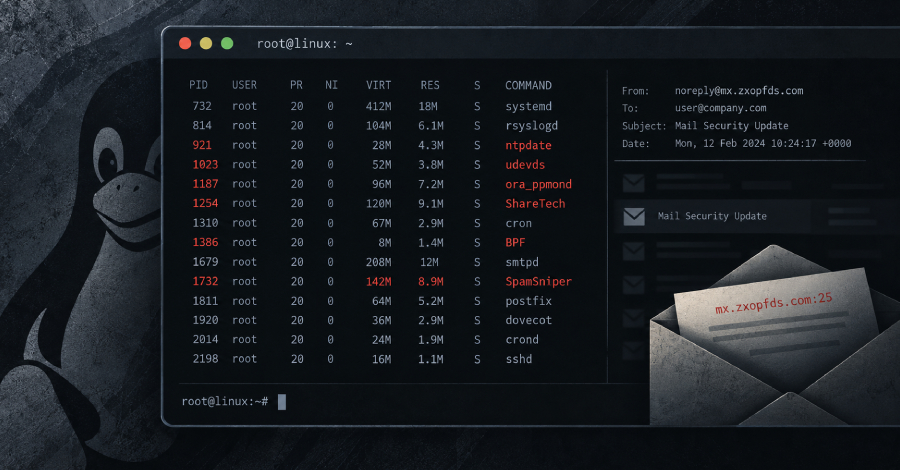
Linux Backdoors Impersonate Email Security Tools to Evade Detection in Korea and Taiwan
Linux backdoors targeting telecom and network appliances in South Korea and Taiwan have been disguising their traffic as email services...
 ENDPUNKTSICHERHEIT
🟠 CVE-2026-105307: High Schwachstelle
A vulnerability was detected in Casdoor up to 3.161.1. Affected is the function ApiFilter of the file routers/authz_filter.go of the...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-19185: High Schwachstelle
The system-call verifier for i3c_do_ccc() in drivers/i3c/i3c_handlers.c validated the outer struct i3c_ccc_payload, the broadcast ccc.data buffer and the targets.payloads[] array,...
 NETZWERKSICHERHEIT
‚NeedyMantis‘ Provides Long-Term Access to Compromised Networks
Microsoft observed a China-based actor using a previously unidentified malware framework in targeted intrusions against telcos, universities, medical, and government-related...
 NETZWERKSICHERHEIT
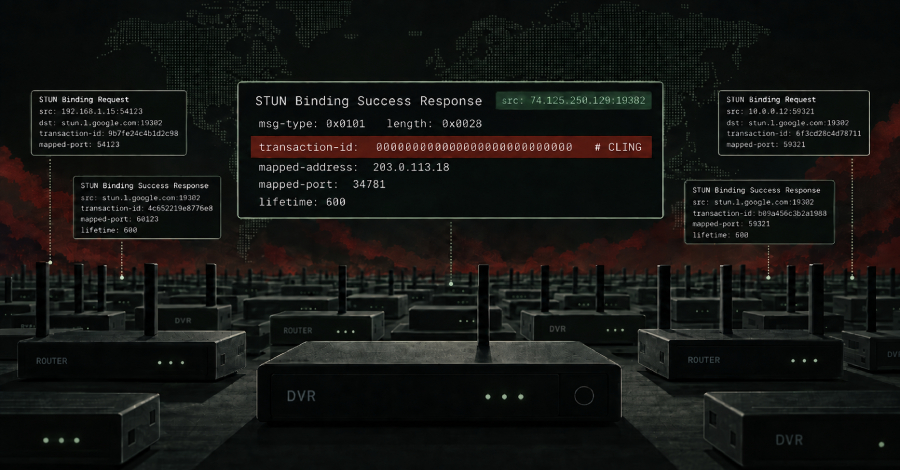
Realtek Jungle SDK Exploit Attempts Deliver Cling Botnet With STUN-Based C2
Threat actors have been observed attempting to exploit a now-patched critical security flaw impacting the Realtek Jungle software development kit...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-105216: High Schwachstelle
go-micro before 6.0.0 contains an improper certificate validation vulnerability that allows network attackers to impersonate services because the shared TLS...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-105295: High Schwachstelle
GitAhead 2.5.0 through 2.7.1 contains an insecure update mechanism that installs downloaded updates without integrity or signature verification and permanently...
 NETZWERKSICHERHEIT
Windows Botnet x47.c Offers AI API Draining, 18 Attack Methods
Qrator found a Windows botnet advertised with AI API draining, credential theft and SOCKS5 proxying...