Netzwerksicherheit
 NETZWERKSICHERHEIT
FBI Seizes NetNut Proxy Platform, Popa Botnet
The Federal Bureau of Investigation (FBI) said today it worked with industry partners to seize hundreds of domains associated with...
 NETZWERKSICHERHEIT
Kubota says hackers had month-long access to network systems
Kubota North America Corporation disclosed that hackers had access to some of its network systems for more than a month...
 NETZWERKSICHERHEIT
FortiBleed credential-theft campaign linked to Lynx ransomware
The massive FortiBleed credential theft campaign has been linked to the INC and Lynx ransomware operations, suggesting the stolen Fortinet...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-10055: High Schwachstelle
In Eclipse Theia since version 1.26.0, the backend /services/request-service RPC accepts an attacker-controlled URL from any client connected to the...
 NETZWERKSICHERHEIT
NetNut proxy network disrupted, 2 million infected devices cut off
A joint operation involving Google has disrupted NetNut, a residential proxy network that gave access to millions of compromised Android...
 NETZWERKSICHERHEIT
AirDrop and Quick Share Flaws Let Nearby Attackers Trigger Crashes and Bypass Checks
Two researchers have found six security flaws in AirDrop and Quick Share, the wireless features that beam files between nearby...
 NETZWERKSICHERHEIT
Phantom Squatting Uses AI-Hallucinated Domains for Phishing and Malware
Large language models keep inventing web addresses that do not exist. Attackers have started buying those made-up domains before anyone...
 NETZWERKSICHERHEIT
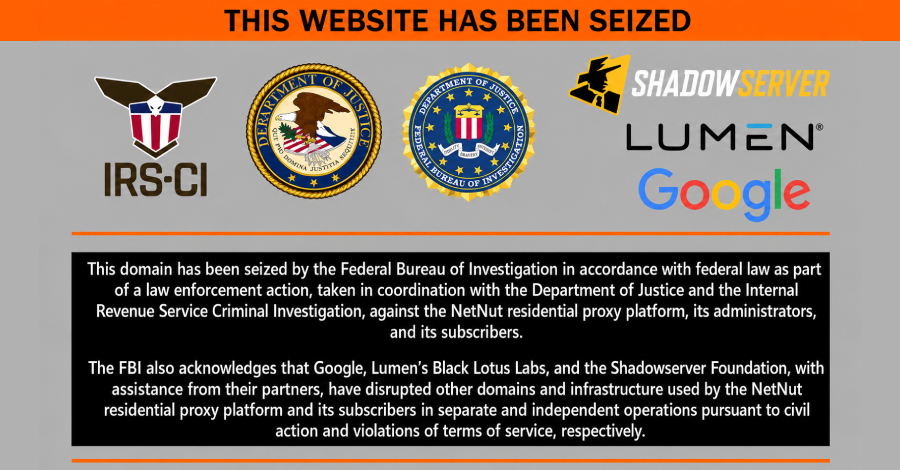
Google Disrupts NetNut Residential Proxy Network Spanning 2 Million Home Devices
Google has significantly degraded NetNut, one of the biggest networks that turns home devices into rented relays for other people's...
NETZWERKSICHERHEIT
🟡 CVE-2026-14258: Medium Schwachstelle
A flaw was found in dhcpcd's IPv6 Neighbor Discovery Router Advertisement processing. A specially crafted IPv6 Router Advertisement containing a...
ANWENDUNGSSICHERHEIT
🔴 CVE-2026-23537: Critical Schwachstelle
A vulnerability has been identified in the Feast Feature Server’s `/save-document` endpoint that allows an unauthenticated remote attacker to write...