Netzwerksicherheit
 NETZWERKSICHERHEIT
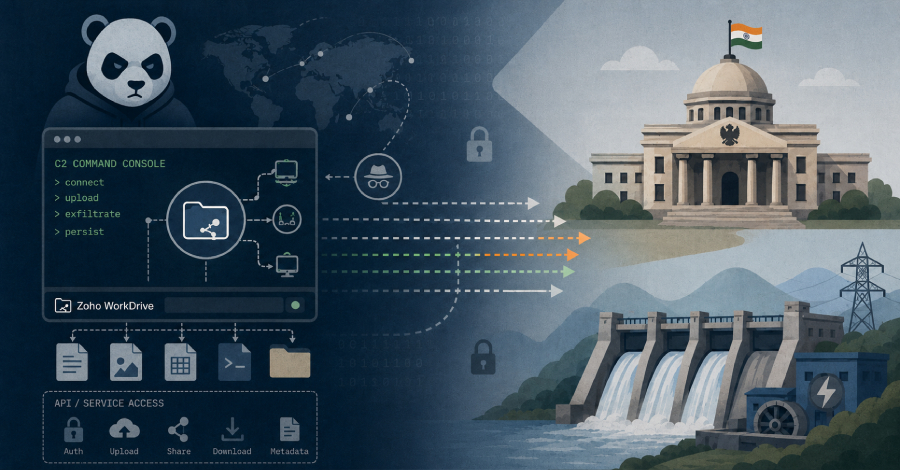
Mustang Panda Uses Zoho WorkDrive as Command Channel in Indian Government Attacks
The China-aligned espionage group Mustang Panda is running two campaigns against the Indian government and hydropower targets, deploying new malware and turning...
 NETZWERKSICHERHEIT
🟡 CVE-2026-13508: Medium Schwachstelle
A flaw has been found in khoj-ai khoj up to 2.0.0-beta.28. This impacts an unknown function of the file src/khoj/routers/api_chat.py...
 NETZWERKSICHERHEIT
US Sanctions Target Cambodian Scam Network Leaders
US sanctions target Cambodian scam networks tied to crypto fraud and trafficking...
 NETZWERKSICHERHEIT
Small Defense Firms Lack Network Data to Stop Nation-State Hackers, Analyst Says
Team Cymru’s Stephen Campbell warned that small US defense contractors are not well prepared to face cyber intrusions through edge...
 NETZWERKSICHERHEIT
🟠 CVE-2026-10646: High Schwachstelle
Zephyr's BSD-sockets getaddrinfo() implementation (subsys/net/lib/sockets/getaddrinfo.c) passes a pointer to a stack-allocated state object (struct getaddrinfo_state ai_state) as the user_data of...
 NETZWERKSICHERHEIT
Fake SSA Emails Drive Venomous#Helper Phishing Campaign
Venomous#Helper attackers impersonate the US Social Security Administration to deploy signed RMM software and maintain persistent access across US networks...
 NETZWERKSICHERHEIT
Legacy Security Tools Failing Data Protection, Capital One Software Report Finds
Traditional network security tools are undermining data protection, with Forrester and Capital One Software research warning AI adoption is impossible...
 NETZWERKSICHERHEIT
🟠 CVE-2026-49486: High Luecke in Apache Apache-Airflow-Providers-Ftp
The Apache Airflow FTP provider's `FTPSHook.get_conn()` created an `ftplib.FTP_TLS` connection but never called `prot_p()`, so although the control channel was...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-2053: High Luecke in Wso2 Api_Manager
The WSO2 API Manager's message flow component, when processing WS-Addressing headers, does not sufficiently validate or restrict user-controlled input within...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-13325: High Schwachstelle
A flaw was found in KubeVirt's migration proxy. When spec.configuration.migrations.disableTLS is set to true on the KubeVirt custom resource, the...