Netzwerksicherheit
 NETZWERKSICHERHEIT
OptinMonster WordPress plugin hacked in CDN supply-chain attack
WordPress plugins OptinMonster, TrustPulse, and PushEngage have been compromised in a supply-chain attack impacting Awesome Motive-s content distribution network (CDN)....
 NETZWERKSICHERHEIT
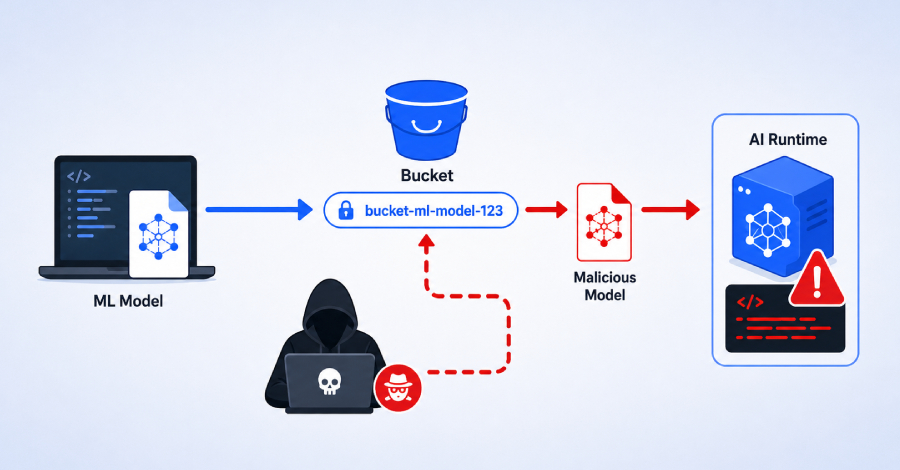
Google Vertex AI SDK Flaw Let Attackers Hijack Model Uploads via Bucket Squatting
A flaw in the Google Cloud Vertex AI SDK for Python let an attacker with no access to a victim's...
 NETZWERKSICHERHEIT
🟡 CVE-2026-9278: Medium Schwachstelle
The Form Builder CP WordPress plugin before 1.2.47 does not properly sanitize a form configuration value before storing it and...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-12223: Medium Schwachstelle
A vulnerability was identified in Yealink SIP-T46U 108.86.0.118. Affected by this vulnerability is the function mod_webd.TFTPUploadIperf of the file /api/inner/tftpuploadiperf...
 NETZWERKSICHERHEIT
🟡 CVE-2025-70102: Medium Schwachstelle
A NULL pointer dereference occurs in Roy Marples NetworkConfiguration/dhcpcd 10.3.0 while parsing configuration options. In parse_option() (src/if-options.c:1886), the code performs...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-47777: High Schwachstelle
Mastodon is a free, open-source social network server based on ActivityPub. In versions there is a missing condition in the...
 NETZWERKSICHERHEIT
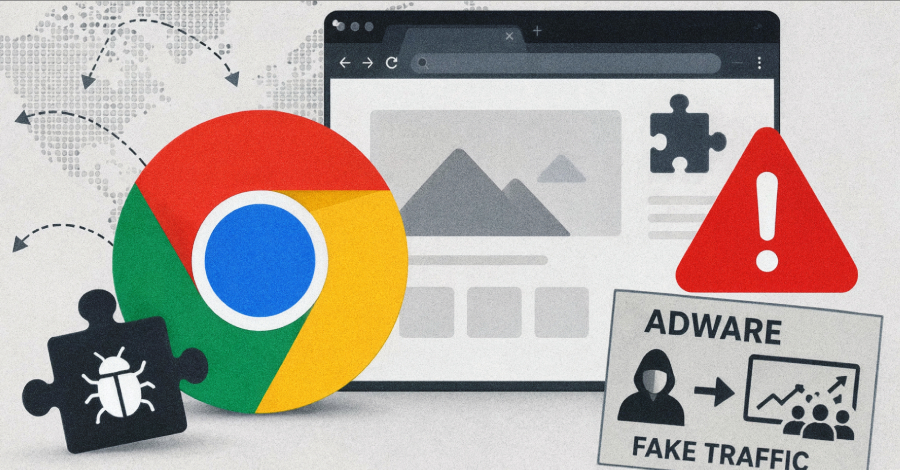
152 Chrome Wallpaper Extensions with 105K Installs Linked to Adware and Fake Traffic
Cybersecurity researchers have discovered a network of 152 Google Chrome extensions that act as new tab live wallpaper add-ons to...
 NETZWERKSICHERHEIT
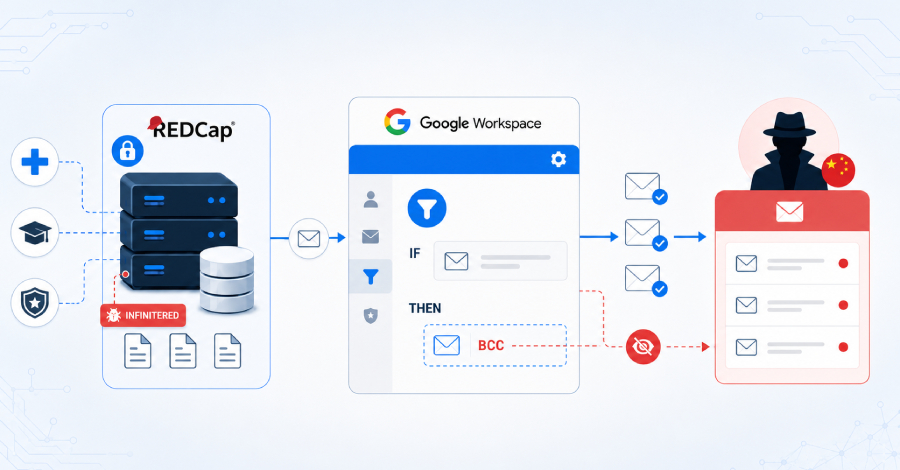
Chinese Hackers Abused Google Workspace Rules to Steal Research and Defense Emails
A China-linked espionage group hid inside North American medical, academic, and military research networks for more than a year, quietly...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-12222: High Schwachstelle
A vulnerability was determined in Yealink SIP-T46U 108.86.0.118. Affected is the function mod_webd.BlueToothTest of the file /api/inner/bttest of the component...
 NETZWERKSICHERHEIT
🟠 CVE-2026-12221: High Schwachstelle
A vulnerability was found in Yealink SIP-T46U 108.86.0.118. This impacts the function sprintf of the file /api/upgrade/upgrade of the component...