Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-12741: High Schwachstelle
The WP Fast Total Search – The Power of Indexed Search plugin for WordPress is vulnerable to generic SQL Injection...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-49332: High Schwachstelle
A flaw was found in openshift/oauth-proxy. The proxy sets authenticated identity headers using only dash-variant keys (X-Forwarded-User) but does not...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-11841: Critical Schwachstelle
An attacker may perform unauthenticated read and write operations on sensitive filesystem areas via the AppEngine Fileaccess over HTTP due...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-16462: Critical Schwachstelle
In PROCON-WEB SCADA the endpoint 'GetGridData' is not properly sanitized. This allows a remote unauthenticated attacker to execute arbitrary SQL...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-15014: Critical Schwachstelle
The SMS Alert – SMS & OTP for WooCommerce, Order Notifications & Abandoned Cart Recovery plugin for WordPress is vulnerable...
 ANWENDUNGSSICHERHEIT
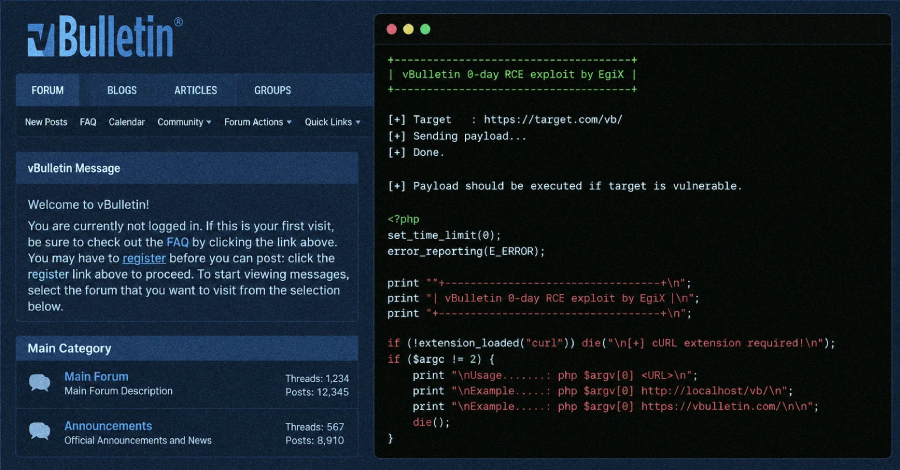
Public Exploit Released for Patched vBulletin Pre-Auth Code Execution Flaw
Public exploit details released on July 27 show how an unauthenticated request can reach PHP's eval() function inside vBulletin and...
 ANWENDUNGSSICHERHEIT
Claude AI Just Cracked a Post-Quantum Test Scheme and Found a Faster 7-Round AES Attack
Anthropic says Claude Mythos Preview helped derive an end-to-end key-recovery attack against HAWK-256 and a 200- to 800-fold speedup for...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-14820: Medium Schwachstelle
The Quiz and Survey Master (QSM) WordPress plugin before 11.1.3 does not implement rate limiting or standard failed-login auditing on...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-17534: Medium Schwachstelle
Kimi Code (@moonshot-ai/kimi-code) before 0.27.0 implements FetchURL SSRF hardening as a static hostname and IP-literal denylist in assertSafeFetchTarget, without resolving...
ANWENDUNGSSICHERHEIT
🟡 CVE-2026-10082: Medium Schwachstelle
The Advanced Ads WordPress plugin before 2.0.23 does not sanitize and escape a shortcode parameter before outputting it in the...