Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-10819: Medium Schwachstelle
Mattermost versions 11.6.x
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-59536: High Schwachstelle
Unauthenticated Broken Access Control in CoCart – Headless ecommerce
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-59530: High Schwachstelle
Unauthenticated Broken Access Control in Stripe For WooCommerce
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-59537: High Schwachstelle
Administrator SQL Injection in Sender – Newsletter, SMS and Email Marketing Automation for WooCommerce
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-59538: Critical Schwachstelle
Unauthenticated SQL Injection in GamiPress
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-59533: Critical Schwachstelle
Unauthenticated SQL Injection in Relevanssi Light
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-59527: Critical Schwachstelle
Unauthenticated SQL Injection in MapSVG
 ANWENDUNGSSICHERHEIT
Attackers Exploit Arista VeloCloud Orchestrator Command Injection Flaw
A maximum-severity security flaw impacting on-premises versions of Arista VeloCloud Orchestrator (VCO) has come under active exploitation in the wild....
 ANWENDUNGSSICHERHEIT
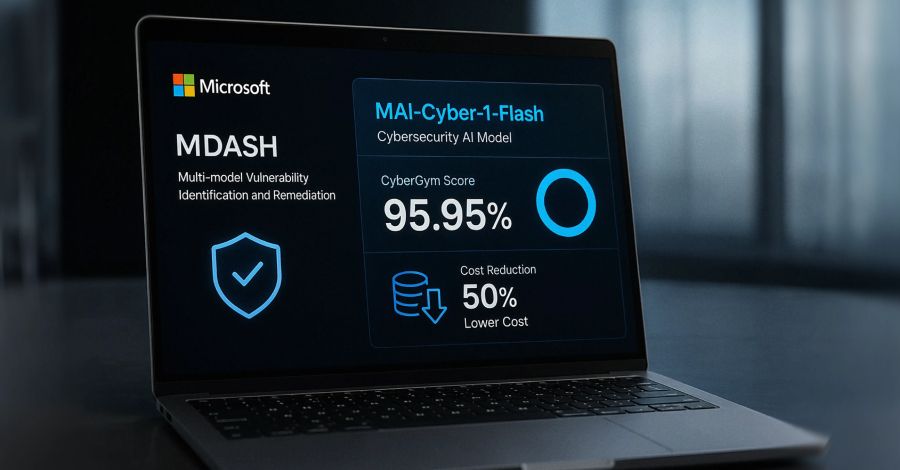
Microsoft Says New Cybersecurity AI Model Helps MDASH Hit 95.95% at Half the Cost
Microsoft has launched its first cybersecurity-specific model inside MDASH, its multi-model vulnerability identification and remediation harness. The company says MDASH,...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-58389: High Luecke in Apache Thrift
Allocation of Resources Without Limits or Throttling vulnerability in Apache Thrift Rust bindings. This issue affects Apache Thrift: before 0.24.0....