Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-12384: High Schwachstelle
Authorization bypass through User-Controlled key vulnerability in TECHIN2B TECHIN2B Application allows Privilege Abuse. This issue affects TECHIN2B Application: from V1.0.7676.13...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-88825: High Schwachstelle
The iGMS Direct Booking WordPress plugin before 2.0 does not authorise or escape its widget appearance settings, allowing unauthenticated users...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-85122: High Schwachstelle
The Easy Form Builder by WhiteStudio WordPress plugin before 4.2.0 does not validate a submitted value against the stored configuration...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-67101: Critical Schwachstelle
HCL BigFix Service Management is affected by a Server-Side Request Forgery (SSRF) vulnerability in its search functionality, which could allow...
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-67100: Critical Schwachstelle
HCL BigFix Service Management is affected by SQL Injection flaw and a Cross-Tenant Data Exposure flaw vulnerabilities. which could allow...
 ANWENDUNGSSICHERHEIT
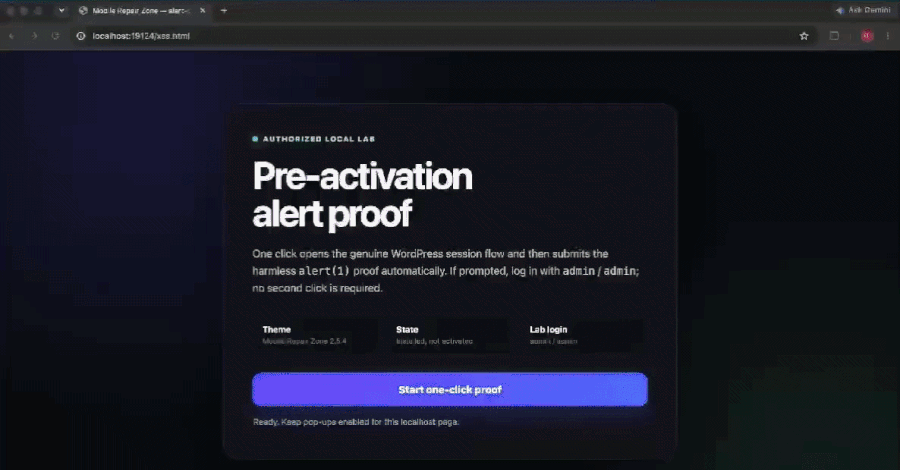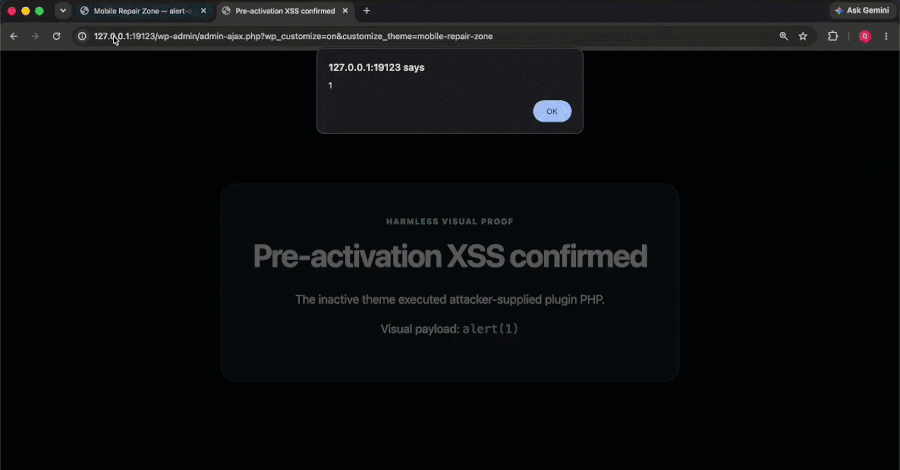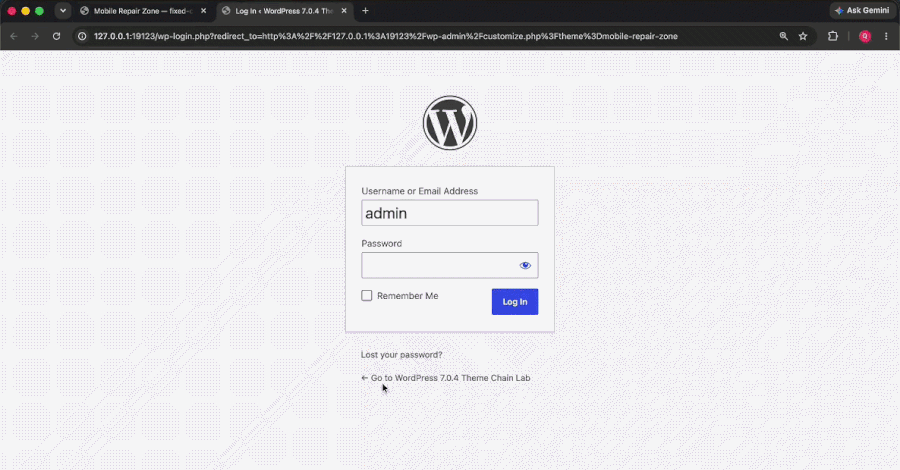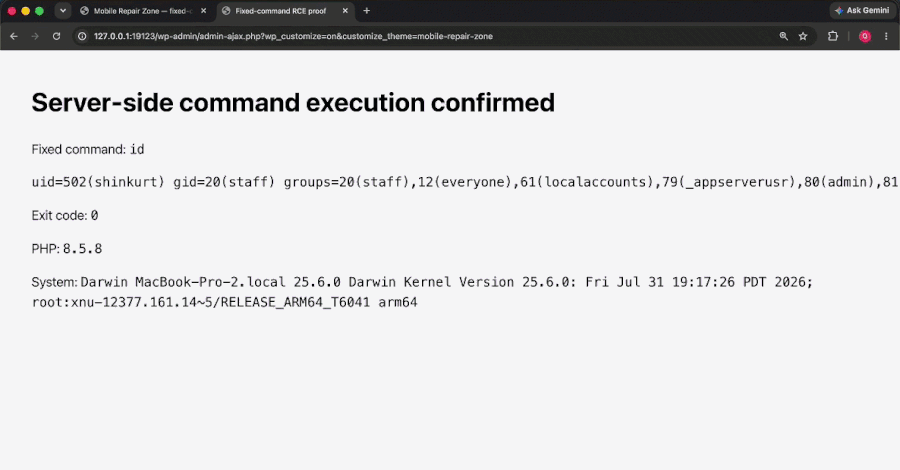
New WordPress Click2Shell Flaw Forces Theme Installs, Can Chain to Code Execution
WordPress today released patches to fix a new set of vulnerabilities in its core software, one of which could allow...
 ANWENDUNGSSICHERHEIT
CISA Flags Three Linux Kernel Vulnerabilities Exploited in the Wild
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added three security flaws impacting the Linux kernel to its...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-92915: High Schwachstelle
WWBN AVideo through commit e01e41ecc (no patched version available) contains a broken access control flaw in objects/userVerifyEmail.php. The script disables...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-92917: High Schwachstelle
Grav is a flat-file CMS. In versions 2.0.0-rc.1 through 2.0.21, the Twig content sandbox fails to restrict the dump and...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-92916: High Schwachstelle
Grav is a flat-file CMS. In Grav 1.7.0 through 1.7.53.2 and 2.0.0 through 2.0.21, when the debugger is enabled (system.debugger.enabled:...