Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-56689: High Schwachstelle
Dell PowerFlex Manager, Version prior to 5.1.0.1, contain(s) an Improper Neutralization of Special Elements used in an SQL Command ('SQL...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-59795: High Schwachstelle
In JetBrains TeamCity before 2026.1.2 stored XSS via unauthenticated agent registration was possible
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-38057: High Schwachstelle
The iDirect iQ200 does not validate CSRF tokens on state-changing API endpoints after authentication. The /api/reboot endpoint accepts POST requests...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-56690: High Schwachstelle
Dell PowerFlex Manager, Version prior to 5.1.0.1, contain(s) an Improper Neutralization of Special Elements used in an SQL Command ('SQL...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-56261: High Schwachstelle
Crawl4AI before 0.8.7 contains a server-side request forgery (SSRF) vulnerability in the Docker API server's /crawl/job and /llm/job endpoints, which...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-54149: High Schwachstelle
MaxKB is an open-source AI assistant for enterprise. Prior to 2.10.0-lts, MaxKB tool import functionality in apps/tools/serializers/tool.py and MCP referencing...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-59793: High Luecke in Jetbrains Teamcity
In JetBrains TeamCity before 2026.1.2 arbitrary file access was possible via the Perforce VCS integration
 ANWENDUNGSSICHERHEIT
🔴 CVE-2026-61444: Critical Schwachstelle
PraisonAI versions before 4.6.78 contain a code injection vulnerability in deploy/api.py where the agents_file parameter is directly interpolated into an...
ANWENDUNGSSICHERHEIT
🔴 CVE-2026-56688: Critical Schwachstelle
Dell PowerFlex Manager, Version prior to 5.1.0.1, contain(s) an Improper Neutralization of Special Elements used in an OS Command ('OS...
 ANWENDUNGSSICHERHEIT
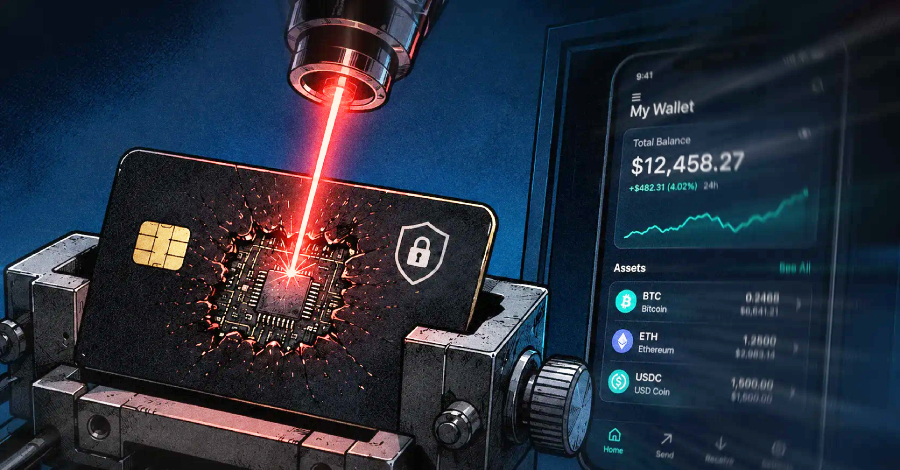
Laser Attack Resets Tangem Wallet Passwords on Cards That Can’t Be Patched
Researchers at Ledger's Donjon security team have shown that a precisely timed laser pulse, aimed at the chip inside a Tangem crypto...