Anwendungssicherheit
 ANWENDUNGSSICHERHEIT
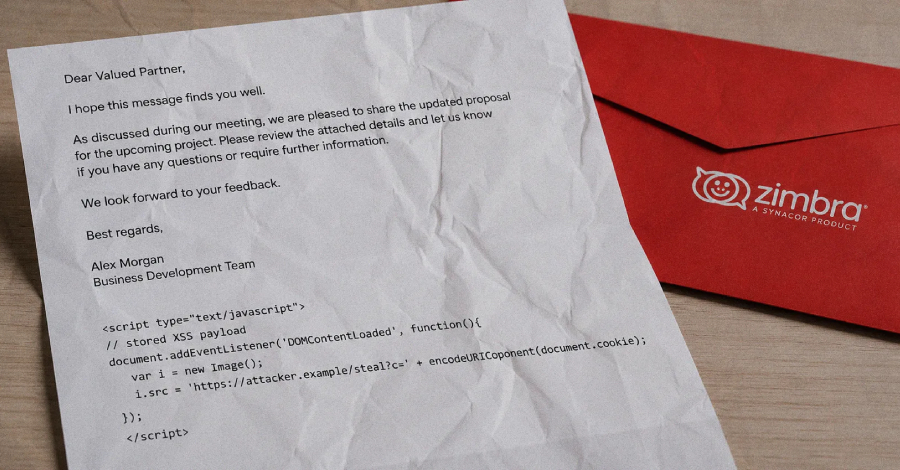
Critical Zimbra Flaw Could Let Crafted Emails Run Malicious Code in User Sessions
Zimbra is urging customers to apply updates to address a critical security vulnerability impacting the Classic Web Client that could...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-13011: Medium Schwachstelle
The ERP: Complete HR, Accounting & CRM Suite with Recruitment and WooCommerce CRM Support plugin for WordPress is vulnerable to...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-13080: Medium Schwachstelle
The WPFunnels – Funnel Builder for WooCommerce with Checkout & One Click Upsell plugin for WordPress is vulnerable to Local...
 ANWENDUNGSSICHERHEIT
🟡 CVE-2026-54799: Medium Schwachstelle
A vulnerability has been identified in CPCI85 Central Processing/Communication (All versions < V26.20), SICORE Base system (All versions < V26.20.0)....
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-54801: High Schwachstelle
A vulnerability has been identified in CPCI85 Central Processing/Communication (All versions < V26.20), SICORE Base system (All versions < V26.20.0)....
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-9253: High Schwachstelle
The WP Cost Estimation & Payment Forms Builder (E&P Forms) plugin for WordPress is vulnerable to Stored Cross-Site Scripting via...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-13441: High Schwachstelle
The EventPrime – Events Calendar, Bookings and Tickets plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the 'new_event_type_background_color'...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-15000: High Schwachstelle
The Connect Contact Form 7 and Mailchimp plugin for WordPress is vulnerable to Stored Cross-Site Scripting via Mailchimp Merge Field...
 ANWENDUNGSSICHERHEIT
🟠 CVE-2026-56292: High Luecke in Acymailing Acymailing
A SQLi vulnerability in AcyMailing component < 10.11.1 for Joomla was discovered. Exploiting this flaw can lead to unauthorized database...
ANWENDUNGSSICHERHEIT
🟠 CVE-2026-57111: High Luecke in Apache Helix
Permissive Cross-Origin Resource Sharing (CORS) in the REST API (helix-rest, org.apache.helix.rest.server.filters.CORSFilter) in Apache Helix through 2.0.0 on all platforms allows...